Fortinet NSE I - OT Security 7.6 Architect
Last Update Oct 14, 2026
Total Questions : 56
We are offering FREE NSEI_OTS_AR-7.6 Fortinet exam questions. All you do is to just go and sign up. Give your details, prepare NSEI_OTS_AR-7.6 free exam questions and then go for complete pool of Fortinet NSE I - OT Security 7.6 Architect test questions that will help you more.
Refer to the exhibit.
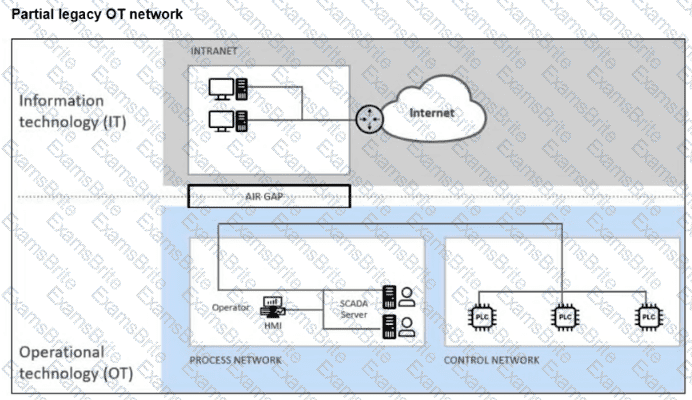
A partial legacy OT network is shown.
You must improve this historically flat OT network and minimize the risk of lateral movement.
Which action must you perform?
Refer to the exhibit.
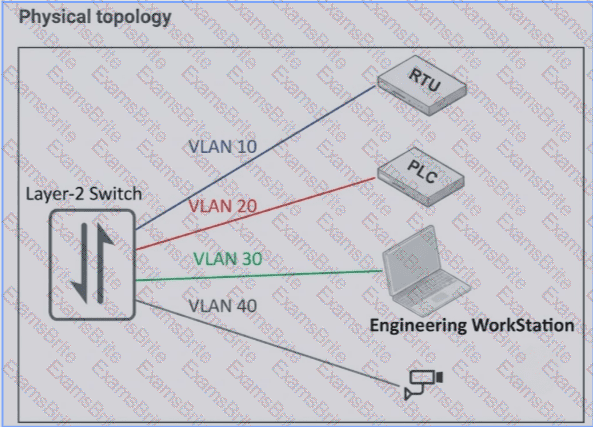
A partial OT network is shown. You have configured the FortiGate device with VLANs to segment the OT network. The supervisor now wants to connect to the PLC from the Engineering Workstation. How can you allow access from the Engineering Workstation to the PLC? (Choose one answer)
You want to protect OT devices that are not updated against known vulnerabilities so you apply virtual patching to the firewall policies. What must you check to confirm that the OT devices are virtually patched? (Choose one answer)
You want to gain complete visibility of the entire attack surface using FortiAnalyzer.
Which two views must you use to achieve this result? (Choose two.)
Refer to the exhibit.
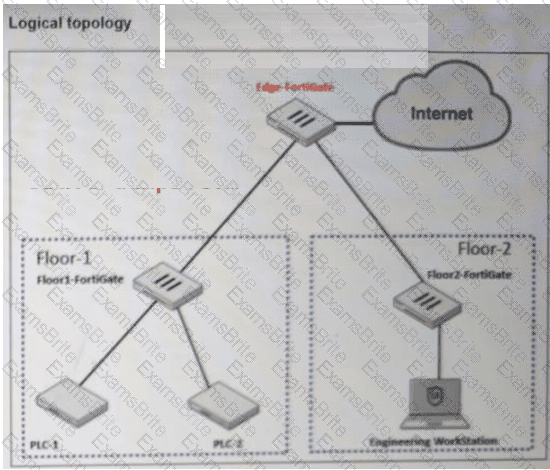
A partial OT network is shown. You have encountered many disconnections in the links and want to improve the availability of this network. Which action can you perform? (Choose one answer)
Refer to the exhibit.
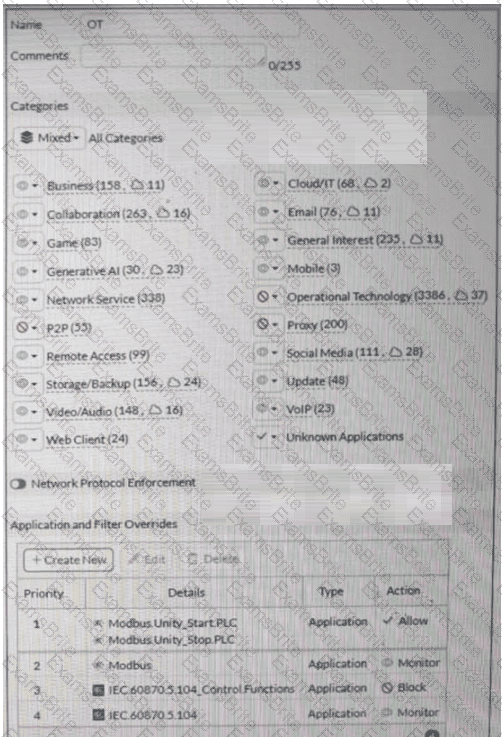
A partial Application Sensor profile is shown. When you apply this profile in a firewall policy, which two statements are correct? (Choose two answers)
Refer to the exhibit.
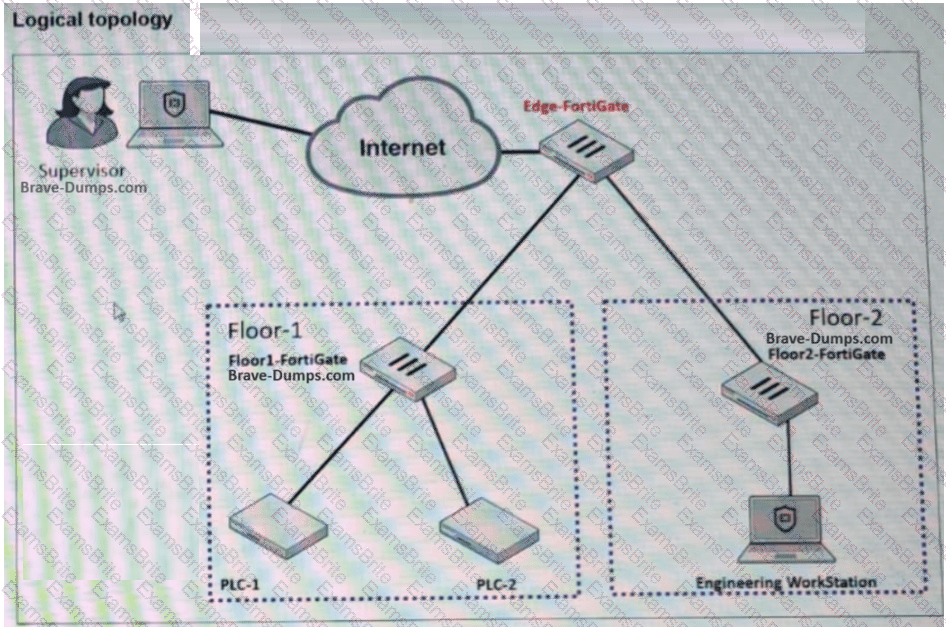
A partial OT network is shown. You want to provide the supervisor with secure remote access. Which two features can you implement on Edge-FortiGate ? (Choose two answers)
Refer to the exhibit.
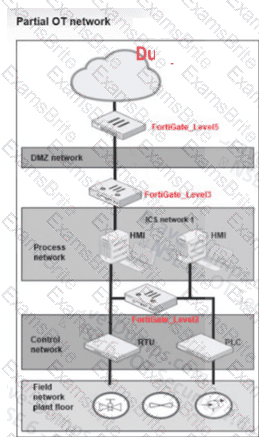
A partial OT network is shown. In this OT network, you must add additional security measures to detect OT protocols and, therefore, increase the traffic visibility. Which security sensor must you implement to detect the OT protocols in this network? (Choose one answer)
Refer to the exhibit.
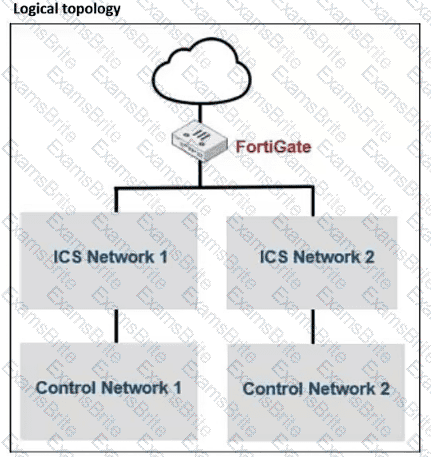
A partial OT network is shown.
The OT network is divided into two main networks with a FortiGate device operating in NAT mode.
How can you further segment network 1 from network 2?
Refer to the exhibits.
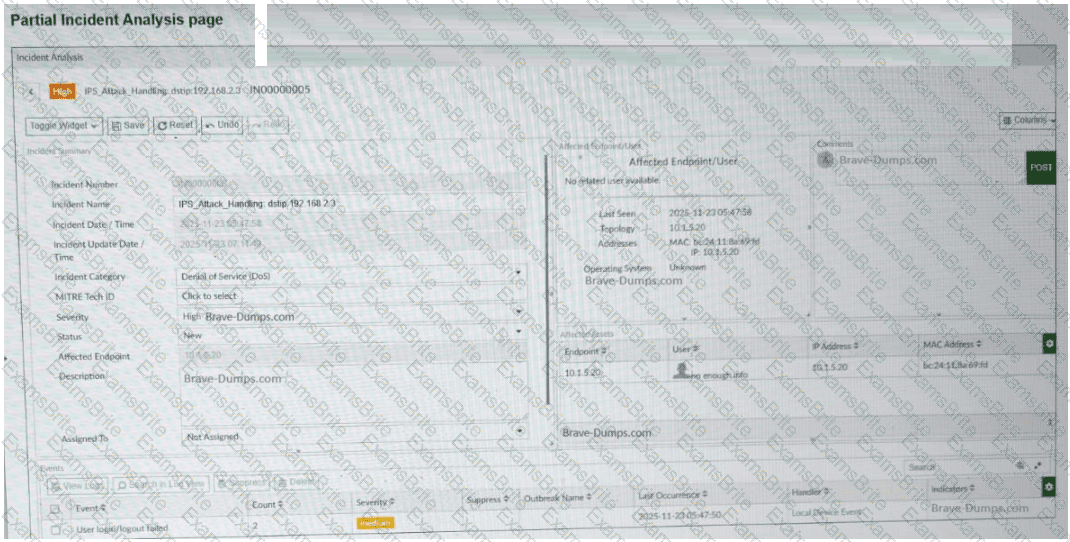
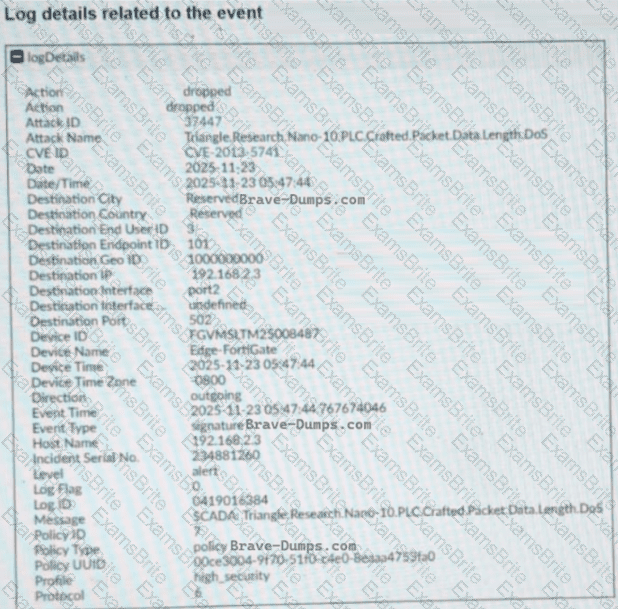
A partial Incident Analysis page and the log details related to the event are shown. An attack is reported on your OT network. You analyze the corresponding incident. Based on the information provided on the Incident Analysis page and the log details, which two statements are correct? (Choose two answers)
Refer to the exhibit.
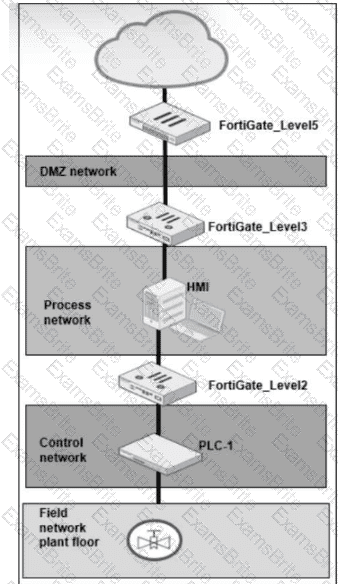
A simplified OT network is shown. You want to optimize the protection of this OT network. Which two controls must you implement? (Choose two answers)
Refer to the exhibit.
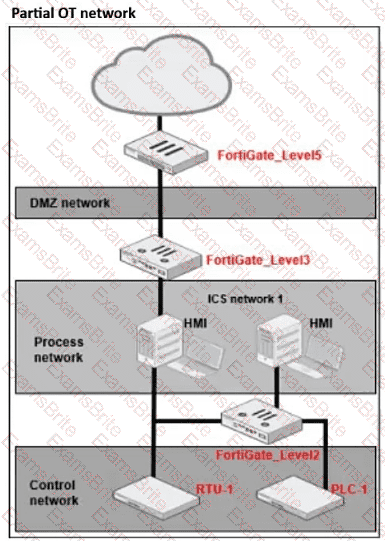
A partial OT network is shown.
PLC-1 has a known critical vulnerability, but you cannot update it.
What must you configure to protect PLC-1?
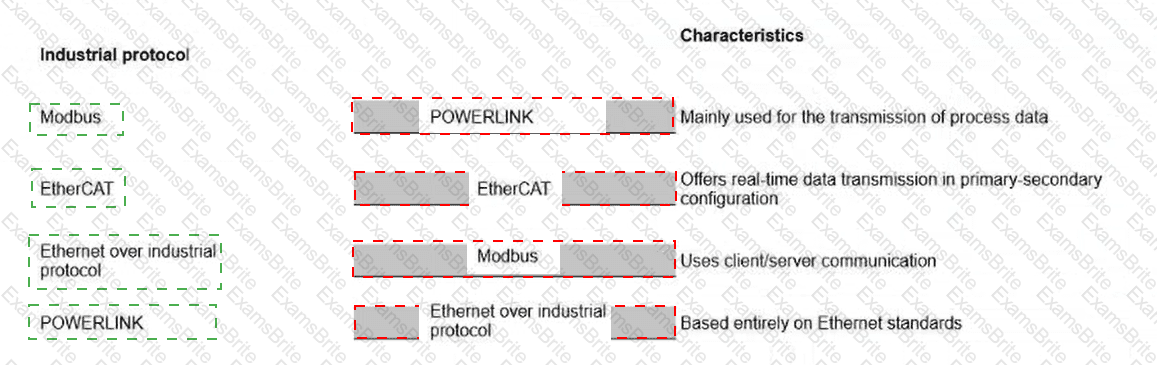
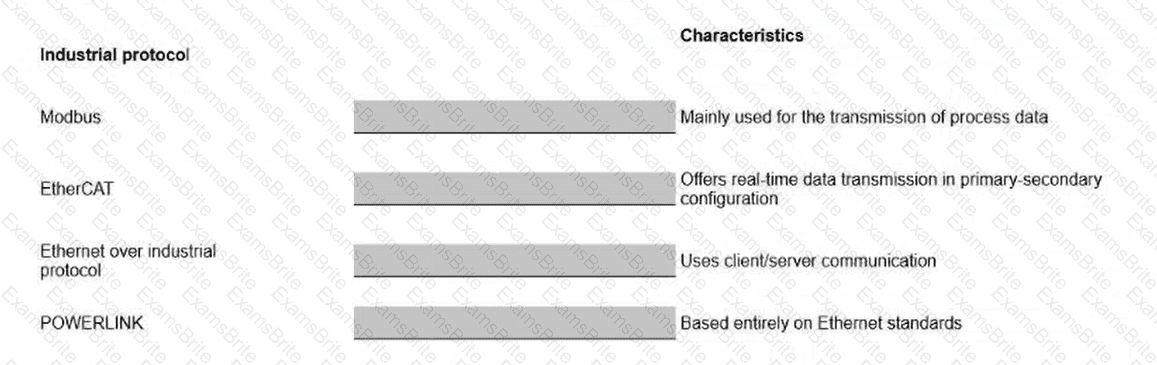
Match each industrial protocol to its corresponding characteristics.
Select each OT industrial protocol in the column on the left and drag and drop it into the blank space next to its corresponding characteristic in the column on the right. You must match all four industrial protocols to their characteristics in the work area.
As the first step in your OT network protection plan, you must identify the OT protocols that the FortiGate device supports. Which two configurations must you implement on this FortiGate device? (Choose two answers)
Refer to the exhibit.
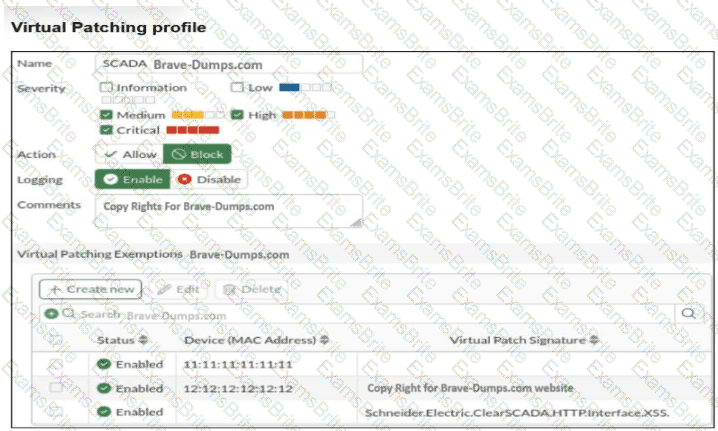
A Virtual Patching profile is shown. You have recently updated your SCADA system and would like to apply the SCADA virtual patching profile. Which two statements about this profile are correct? (Choose two answers)
Refer to the exhibit.
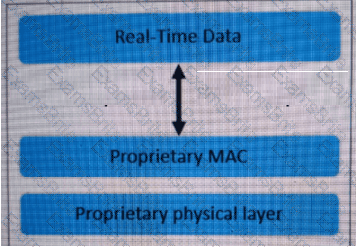
An industrial Ethernet protocol skipping layers 3 to 6 is shown. Which industrial Ethernet protocol is it? (Choose one answer)
TESTED 15 Oct 2026