Pre-Winter Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: agile70

ExamsBrite Dumps

Fortinet NSE 7 - Public Cloud Security 7.6.4 Architect Question and Answers

Fortinet NSE 7 - Public Cloud Security 7.6.4 Architect

Last Update Oct 14, 2026
Total Questions : 67

We are offering FREE NSE7_CDS_AR-7.6 Fortinet exam questions. All you do is to just go and sign up. Give your details, prepare NSE7_CDS_AR-7.6 free exam questions and then go for complete pool of Fortinet NSE 7 - Public Cloud Security 7.6.4 Architect test questions that will help you more.
NSE7_CDS_AR-7.6 pdf

NSE7_CDS_AR-7.6 PDF

$31.5  $104.99
NSE7_CDS_AR-7.6 Engine

NSE7_CDS_AR-7.6 Testing Engine

$37.5  $124.99
NSE7_CDS_AR-7.6 PDF + Engine

NSE7_CDS_AR-7.6 PDF + Testing Engine

$49.5  $164.99
Questions 1

You are using Ansible to modify the configuration of several FortiGate VMs. What is the minimum number of files you need to create, and in which file should you configure the target FortiGate IP addresses?

Options:

A.  

One playbook file for each target and the required tasks, and one inventory file.

B.  

One .yaml file with the targets IP addresses, and one playbook file with the tasks.

C.  

One inventory file for each target device, and one playbook file.

D.  

One text file for all target devices, and one playbook file.

Discussion 0
Questions 2

You are automating configuration changes on one of the FortiGate VMs using Red Hat Ansible.

How does Red Hat Ansible connect to FortiGate to make the configuration change?

Options:

A.  

It uses a FortiGate VIP.

B.  

It uses an API.

C.  

It uses SSH.

D.  

It uses a YAML file.

Discussion 0
Questions 3

Your DevOps team is evaluating different Infrastructure as Code (IaC) solutions for deploying complex Azure environments.

What is an advantage of choosing Azure Bicep over other IaC tools available?

Options:

A.  

Azure Bicep generates deployment logs that are optimized to improve error handling.

B.  

Azure Bicep provides immediate support for all Azure services, including those in preview.

C.  

Azure Bicep requires less frequent schema updates than Azure Resource Manager (ARM) templates.

D.  

Azure Bicep can reduce deployment costs by limiting resource utilization during testing.

Discussion 0
Questions 4

In an SD-WAN TGW Connect topology, which three initial steps are mandatory when routing traffic from a spoke VPC to a security VPC through a Transit Gateway? (Choose three.)

Options:

A.  

From the security VPC TGW subnet routing table, point 0.0.0.0/0 traffic to the FortiGate internal port.

B.  

From the security VPC TGW subnet routing table, point 0.0.0.0/0 traffic to the TGW.

C.  

From both spoke VPCs, and the security VPC, point 0.0.0.0/0 traffic to the Internet Gateway.

D.  

From the security VPC FortiGate internal subnet routing table, point 0.0.0.0/0 traffic to the TGW.

E.  

From the spoke VPC internal routing table, point 0.0.0.0/0 traffic to the TGW.

Discussion 0
Questions 5

A VM in Azure is failing to communicate with other VMs in the same subnet.

What is the most likely cause?

Options:

A.  

There is at least one user-defined route blocking traffic within the subnet.

B.  

Some of the VMs are beyond your allowed quota for the Azure region.

C.  

A network security group (NSG) has overridden the default intrasubnet communication rule.

D.  

The VMs do not have a public IP address configured.

Discussion 0
Questions 6

An administrator is configuring a software-defined network (SDN) connector in FortiWeb to dynamically obtain information about existing objects in an Amazon Elastic Kubernetes Service (EKS) cluster.

Which AWS policy should the administrator attach to a user to achieve this goal?

Options:

A.  

AmazonEKSConnectorServiceRolePolicy

B.  

AmazonEKSComputePolicy

C.  

AmazonEKSServicePolicy

D.  

AmazonEKSClusterPolicy

Discussion 0
Questions 7

The cloud administration team is reviewing an AWS deployment that was done using CloudFormation.

The deployment includes six FortiGate instances that required custom configuration changes after being deployed. The team notices that unwanted traffic is reaching some of the FortiGate instances because the template is missing a security group.

To resolve this issue, the team decides to update the JSON template with the missing security group and then apply the updated template directly, without using a change set.

What is the result of following this approach?

Options:

A.  

If new FortiGate instances are deployed later they will include the updated changes.

B.  

Some of the FortiGate instances may be deleted and replaced with new copies.

C.  

The update is applied, and the security group is added to all instances without interruption.

D.  

CloudFormation rejects the update and warns that a new full stack is required.

Discussion 0
Questions 8

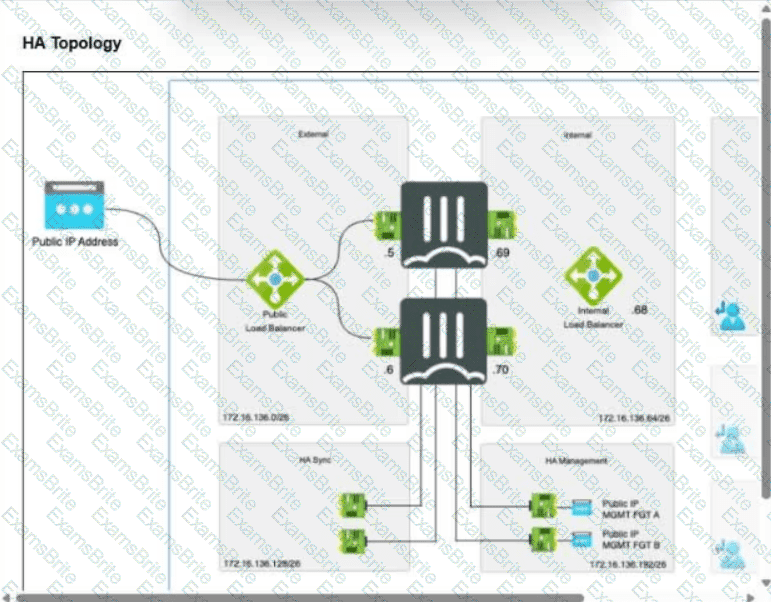
Refer to the exhibit.

Consider the active-active load balance sandwich scenario in Microsoft Azure.

What are two important facts in the active-active load balance sandwich scenario? (Choose two.)

Options:

A.  

It is recommended to enable NAT on FortiGate policies.

B.  

It uses the FGCP protocol for session synchronization by default.

C.  

It uses the vdom-exception command to exclude the configuration from being synchronized by default.

D.  

It supports session synchronization for handling asymmetric traffic.

Discussion 0
Questions 9

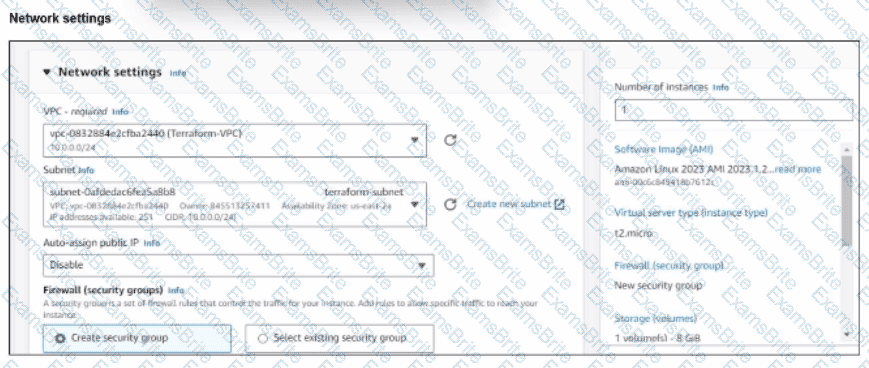
Refer to the exhibit.

You have deployed a Linux EC2 instance in Amazon Web Services (AWS) with the settings shown on the exhibit.

What next step must the administrator take to access this instance from the internet?

Options:

A.  

Allocate an Elastic IP address and assign it to the instance.

B.  

Create a VIP on FortiGate to allow access.

C.  

Enable SSH and allocate it to the device.

D.  

Configure the user name and password.

Discussion 0
Questions 10

Which statement about Transit Gateway (TGW) in Amazon Web Services (AWS) is true?

Options:

A.  

Both the TGW attachment and propagation must be in the same TGW route table.

B.  

TGW can have multiple TGW route tables.

C.  

A TGW attachment can be associated with multiple TGW route tables.

D.  

The TGW default route table cannot be disabled.

Discussion 0
Questions 11

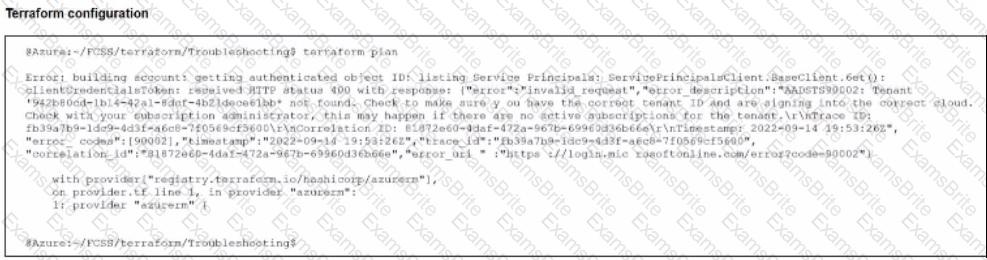
Refer to the exhibit.

After the initial Terraform configuration in Microsoft Azure, the terraform plan command is run.

Which two statements about running the terraform plan command are true? (Choose two.)

Options:

A.  

The terraform plan command will deploy the rest of the resources except the service principle details.

B.  

You cannot run the terraform apply command before the terraform plan command.

C.  

The terraform plan command makes terraform do a dry run.

D.  

You must run the terraform init command once, before the terraform plan command.

Discussion 0
Questions 12

Your administrator instructed you to deploy an Azure vWAN solution to create a connection between the main company site and branch sites to the other company VNETs. What is the best connection solution available between your company headquarters, branch sites, and the Azure vWAN hub? (Choose one answer)

Options:

A.  

An L2TP connection

B.  

SSL VPN connections

C.  

GRE tunnels

D.  

ExpressRoute

Discussion 0
Questions 13

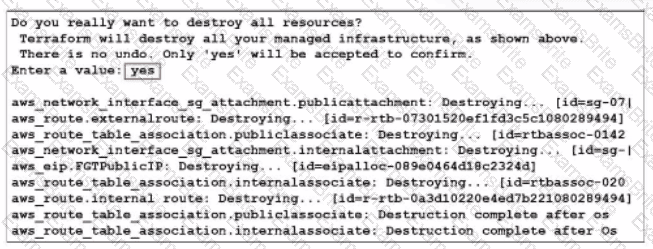
What would be the impact of confirming to delete all the resources in Terraform?
Options:

A.  

It destroys all the resources tied to the AWS Identity and Access Management (IAM) user.

B.  

It destroys all the resources in the resource group.

C.  

It destroys all the resources in the .tfstate file.

D.  

It destroys all the resources in the .tfvars file.

Discussion 0
Questions 14

What are two main features in Amazon Web Services (AWS) network access control lists (NACLs)? (Choose two answers)

Options:

A.  

NACLs are stateless, and inbound and outbound rules are used for traffic filtering.

B.  

NACLs are tied to an instance.

C.  

The default NACL is configured to allow all traffic.

D.  

You cannot use NACLs and Security Groups at the same time.

Discussion 0
Questions 15

Refer to the exhibit.

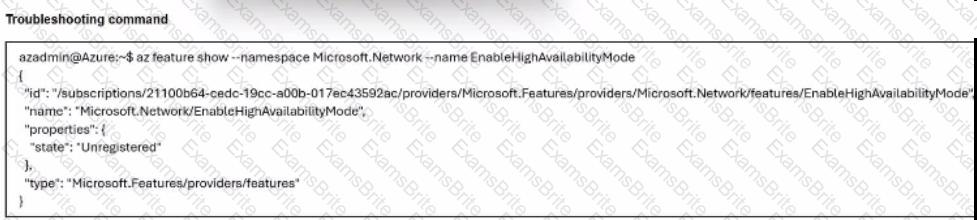
A managed security service provider (MSSP) administration team is trying to deploy a new HA cluster in Azure to filter traffic to and from a client that is also using Azure. However, every deployment attempt fails, and only some of the resources are deployed successfully. While troubleshooting this issue, the team runs the command shown in the exhibit.

What are the implications of the output of the command?

Options:

A.  

The team will not be able to deploy an A-P FortiGate HA cluster with Azure gateway load balancer.

B.  

The team will not be able to deploy an A-P FortiGate HA cluster with Azure load balancer.

C.  

The team will not be able to deploy an active-passive (A-P) FortiGate high availability (HA) cluster with SDN connector.

D.  

The team will not be able to deploy an active-active (A-P) FortiGate HA cluster with Azure load balancer.

Discussion 0
Questions 16

An administrator implements FortiWeb ingress controller to protect containerized web applications in an AWS Elastic Kubernetes Service (EKS) cluster.
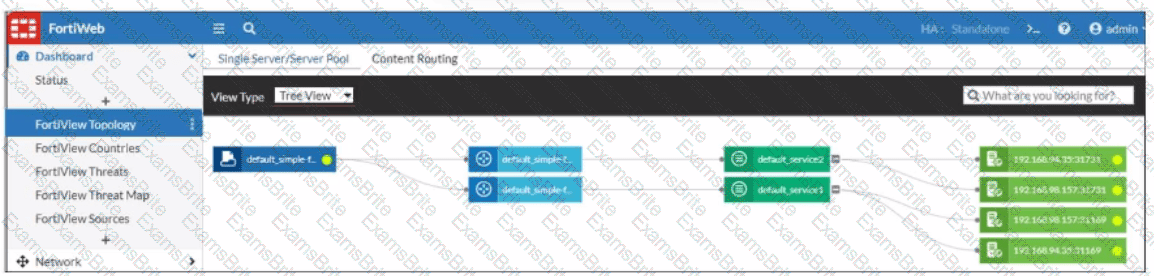
What can you conclude about the topology shown in FortiView?

Options:

A.  

The FortiWeb VM gets the latest cluster information through an SDN connector.

B.  

This topology has two services and two ingress controllers deployed.

C.  

Both services will be load balanced among the two nodes and the four pods.

D.  

Adding a new service will update the FortiWeb configuration automatically.

Discussion 0
Questions 17

A Network security administrator is searching for a solution to secure traffic going in and out of the container infrastructure.

In which two ways can Fortinet container security help secure container infrastructures? (Choose two.)

Options:

A.  

FortiGate NGFW can inspect north-south container traffic with label aware policies.

B.  

FortiGate NGFW and FortiWeb can be used to secure container traffic.

C.  

FortiGate NGFW can connect to the worker nodes and protect the containers.

D.  

FortiGate NGFW can be placed between each application container for north-south traffic inspection.

Discussion 0
Questions 18

Refer to the exhibit.

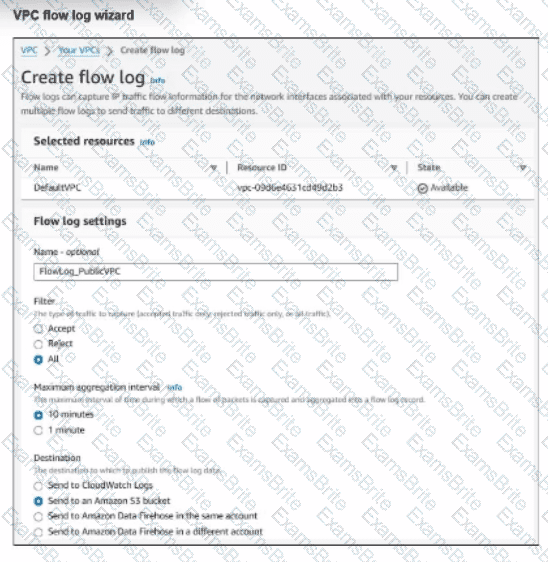
An experienced AWS administrator is creating a new virtual public cloud (VPC) flow log with the settings shown in the exhibit.

What is the purpose of this configuration?

Options:

A.  

To maximize the number of logs saved

B.  

To monitor logs in real time

C.  

To retain logs for a long term

D.  

To troubleshoot a log flow issue

Discussion 0
Questions 19

Exhibit.

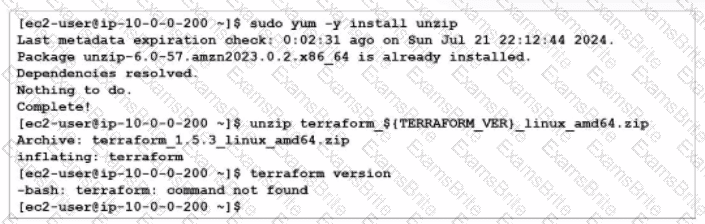
You are tasked with deploying FortiGate using Terraform. When you run the terraform version command during the Terraform installation, you get an error message.

What could you do to resolve the command not found error?

Options:

A.  

You must move the binary file to the bin directory.

B.  

You must reinstall Terraform.

C.  

You must change the directory location to the root directory.

D.  

You must assign correct permissions to the ec2-user.

Discussion 0
Questions 20

You are experiencing intermittent connectivity issues in a FortiGate HA cluster deployed with Azure gateway load balancer. Traffic is being dropped when it passes through the cluster. What is the cause of the issue? (Choose one answer)1
Options:

A.  

The FortiGate firewalls are using the default maximum transmission unit (M2TU) size supported by Azure.

B.  

The Azure gateway load balancer is configured with an incorrect health probe port.

C.  

The Azure gateway load balancer is blocking large packets, causing traffic failures.

D.  

The protected VMs are running an application that fragments packets.

Discussion 0