Pre-Winter Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: agile70

ExamsBrite Dumps

Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Question and Answers

Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator

Last Update Oct 14, 2026
Total Questions : 50

We are offering FREE NSE5_SSE_AD-7.6 Fortinet exam questions. All you do is to just go and sign up. Give your details, prepare NSE5_SSE_AD-7.6 free exam questions and then go for complete pool of Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator test questions that will help you more.
NSE5_SSE_AD-7.6 pdf

NSE5_SSE_AD-7.6 PDF

$31.5  $104.99
NSE5_SSE_AD-7.6 Engine

NSE5_SSE_AD-7.6 Testing Engine

$37.5  $124.99
NSE5_SSE_AD-7.6 PDF + Engine

NSE5_SSE_AD-7.6 PDF + Testing Engine

$49.5  $164.99
Questions 1

Which two methods are available for provisioning FortiClient on endpoints using FortiSASE? (Choose two.)

Options:

A.  

FortiClient can be provisioned using SCCM or GPO, but only through an external portal and not through the FortiSASE portal.

B.  

FortiClient can be provisioned using installers with an invitation code from the FortiSASE portal and deployed through SCCM or GPO, or mobile device management (MDM) software.

C.  

FortiClient can be provisioned by distributing the installer to end users for manual installation.

D.  

FortiClient provisioning is limited to using mobile device management (MDM) software or manual installation without requiring an invitation code.

E.  

FortiClient can be provisioned only by distributing installers to end users through the FortiSASE portal without an invitation code.

Discussion 0
Questions 2

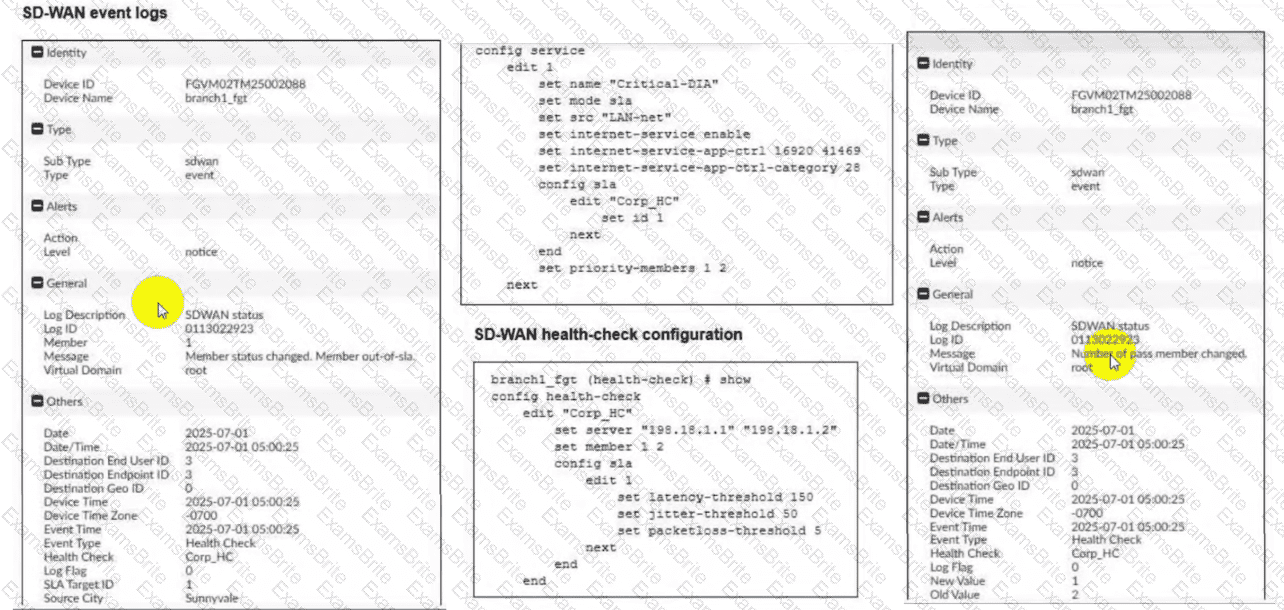
Refer to the exhibits.

Two SD-WAN event logs, the member status, the SD-WAN rule configuration, and the health-check configuration for a FortiGate device are shown. Immediately after the log messages are displayed, how will the FortiGate steer the traffic based on the information shown in the exhibits? (Choose one answer)

Options:

A.  

FortiGate uses port1 or port2 to steer the traffic for SD-WAN rule ID 1.

B.  

FortiGate uses port1 to steer the traffic for SD-WAN rule ID 1.

C.  

FortiGate uses port2 to steer the traffic for SD-WAN rule ID 1.

D.  

FortiGate skips SD-WAN rule ID 1.

Discussion 0
Questions 3

Which two statements correctly describe what happens when traffic matches the implicit SD-WAN rule? (Choose two answers)

Options:

A.  

Traffic is load balanced using the algorithm set for the v4-ecmp-mode setting.

B.  

Traffic does not match any of the entries in the policy route table.

C.  

FortiGate flags the session with may_dirty and vwl_default.

D.  

The traffic is distributed, regardless of weight, through all available static routes.

E.  

The session information output displays no SD-WAN service id.

Discussion 0
Questions 4

How is the Geofencing feature used in FortiSASE? (Choose one answer)

Options:

A.  

To allow or block remote user connections to FortiSASE POPs from specific countries.

B.  

To restrict access to applications based on the time of day in specific countries.

C.  

To encrypt data at rest on mobile devices in specific countries.

D.  

To monitor user behavior on websites and block non-work-related content from specific countries

Discussion 0
Questions 5

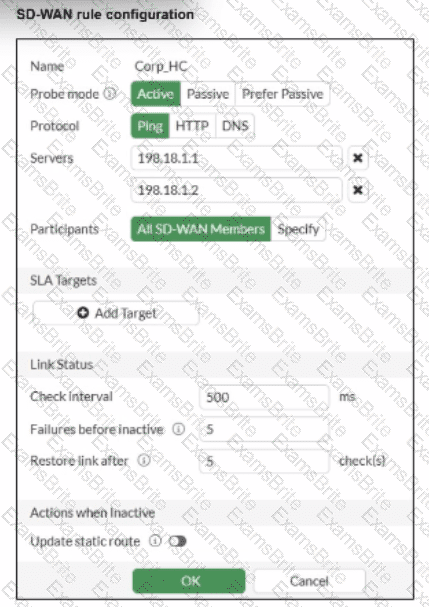
Refer to the exhibit.

You want the performance service-level agreement (SLA) to measure the jitter of each member. Which configuration change must you make to achieve this result?

Options:

A.  

No change is required.

B.  

Add an SLA target and define a jitter threshold.

C.  

Specify the participant members.

D.  

Set the protocol to HTTP.

Discussion 0
Questions 6

You want FortiGate to use SD-WAN rules to steer ping local-out traffic. Which two constraints should you consider? (Choose two.)

Options:

A.  

You must configure each local-out feature individually to use SD-WAN.

B.  

By default, FortiGate uses SD-WAN rules only for local-out traffic that corresponds to ping and traceroute.

C.  

You can steer local-out traffic only with SD-WAN rules that use the manual strategy.

D.  

By default, FortiGate uses SD-WAN rules only for local-out traffic that corresponds to ping and traceroute.

Discussion 0
Questions 7

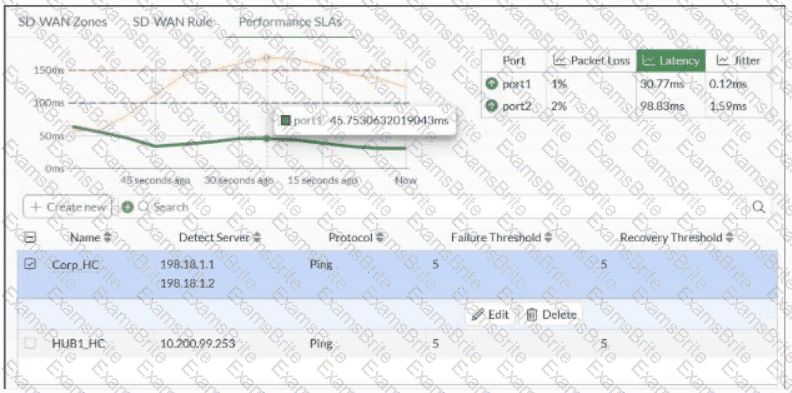
Refer to the exhibit.

Which conclusion can you draw from the exhibit?

Options:

A.  

Over the past 60 seconds, the member port2 latency was temporarily above the latency criteria defined for HUB1_HC.

B.  

The administrator configured the Corp_HC performance service-level agreement (SLA) with SLA targets for the three criteria: packet loss, latency, and jitter.

C.  

Over the past 60 seconds, the member port1 was monitored healthy for both latency criteria of the Corp_HC definition.

D.  

The administrator configured the packet loss threshold for Corp_HC and HUB1_HC to 5%.

Discussion 0
Questions 8

The IT team is wondering whether they will need to continue using MDM tools for future FortiClient upgrades.

What options are available for handling future FortiClient upgrades?

Options:

A.  

Enable the Endpoint Upgrade feature on the FortiSASE portal.

B.  

FortiClient will need to be manually upgraded.

C.  

Perform onboarding for managed endpoint users with a newer FortiClient version.

D.  

A newer FortiClient version will be auto-upgraded on demand.

Discussion 0
Questions 9

Which secure internet access (SIA) use case minimizes individual endpoint configuration? (Choose one answer)

Options:

A.  

Agentless remote user internet access

B.  

SIA for FortiClient agent remote users

C.  

Site-based remote user internet access

D.  

SIA using ZTNA

Discussion 0
Questions 10

An existing Fortinet SD-WAN customer who has recently deployed FortiSASE wants to have a comprehensive view of, and combined reports for, both SD-WAN branches and remote users. How can the customer achieve this?

Options:

A.  

Forward the logs from FortiSASE to Fortinet SOCaaS.

B.  

Forward the logs from FortiGate to FortiSASE.

C.  

Forward the logs from FortiSASE to the external FortiAnalyzer.

D.  

Forward the logs from the external SD-WAN FortiAnalyzer to FortiSASE.

Discussion 0
Questions 11

What is the primary purpose of implementing a dedicated IP in security POPs?

Options:

A.  

To improve website performance by reducing load times

B.  

To provide a unique identifier for logging and monitoring user activities across multiple networks

C.  

To ensure consistent and reliable access for specific users or devices

D.  

To implement geolocation rules and source IP address anchoring

Discussion 0
Questions 12

Which three challenges in a work-from-anywhere environment does FortiSASE address? (Choose three.)

Options:

A.  

Inconsistent security levels

B.  

Lack of bandwidth

C.  

Lack of visibility and control

D.  

Poor performance

E.  

Remote internet connectivity

Discussion 0
Questions 13

Which three reports are valid report types in FortiSASE? (Choose three.)

Options:

A.  

Web Usage Summary Report

B.  

Endpoint Compliance Deviation Report

C.  

Vulnerability Assessment Report

D.  

Shadow IT Report

E.  

Cyber Threat Assessment

Discussion 0
Questions 14

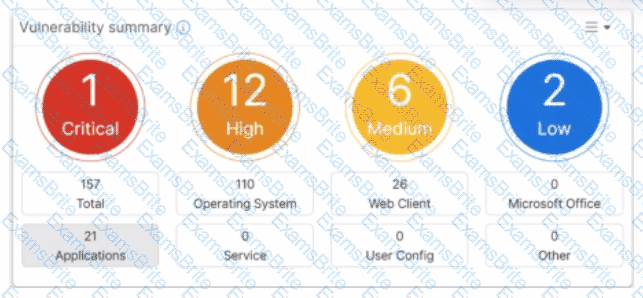
Refer to the exhibit.

Which two statements about the Vulnerability summary dashboard in FortiSASE are correct? (Choose two.)

Options:

A.  

The dashboard shows the vulnerability score for unknown applications.

B.  

Vulnerability scan is disabled in the endpoint profile.

C.  

The dashboard allows the administrator to drill down and view CVE data and severity classifications.

D.  

Automatic vulnerability patching can be enabled for supported applications.

Discussion 0
Questions 15

Refer to the exhibits.

The administrator increases the member priority on port2 to 20. Upon configuration changes and the receipt of new packets, which two actions does FortiGate perform on existing sessions established over port2? (Choose two.)
Options:

A.  

FortiGate updates the gateway information of the sessions with SNAT so that they use port1 instead of port2.

B.  

FortiGate flags the SNAT session as dirty only if the administrator has assigned an IP pool to the firewall policies with NAT.

C.  

FortiGate routes only new sessions over port1.

D.  

FortiGate continues routing all existing sessions over port2.

E.  

FortiGate flags the sessions as dirty.

Discussion 0