Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)
Last Update Sep 16, 2026
Total Questions : 801
We are offering FREE 350-701 Cisco exam questions. All you do is to just go and sign up. Give your details, prepare 350-701 free exam questions and then go for complete pool of Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) test questions that will help you more.
A network engineer has configured a NTP server on a Cisco ASA. The Cisco ASA has IP reachability to the
NTP server and is not filtering any traffic. The show ntp association detail command indicates that the
configured NTP server is unsynchronized and has a stratum of 16. What is the cause of this issue?
A company is experiencing exfiltration of credit card numbers that are not being stored on-premise. The
company needs to be able to protect sensitive data throughout the full environment. Which tool should be used
to accomplish this goal?
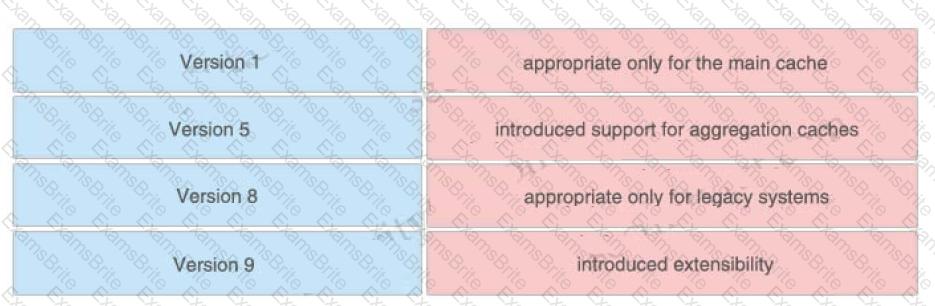
Drag and drop the NetFlow export formats from the left onto the descriptions on the right.
When Cisco and other industry organizations publish and inform users of known security findings and
vulnerabilities, which name is used?
What is a benefit of using telemetry over SNMP to configure new routers for monitoring purposes?
A security engineer must configure a Splunk Universal Forwarder to send network traffic logs from Cisco Catalyst switches to a Splunk indexer cluster. Strict compliance requirements require all network traffic logs to be ingested into Splunk as an audit trail. The environment includes thousands of forwarders, and the data must be distributed across all indexers. Which two configuration actions must be performed? (Choose two.)
What does endpoint isolation in Cisco AMP for Endpoints security protect from?
An administrator needs to configure the Cisco ASA via ASDM such that the network management system
can actively monitor the host using SNMPv3. Which two tasks must be performed for this configuration?
(Choose two.)
An engineer configured a new network identity in Cisco Umbrella but must verify that traffic is being routed
through the Cisco Umbrella network. Which action tests the routing?
Which technology limits communication between nodes on the same network segment to individual applications?
An organization has noticed an increase in malicious content downloads and wants to use Cisco Umbrella to prevent this activity for suspicious domains while allowing normal web traffic. Which action will accomplish this task?
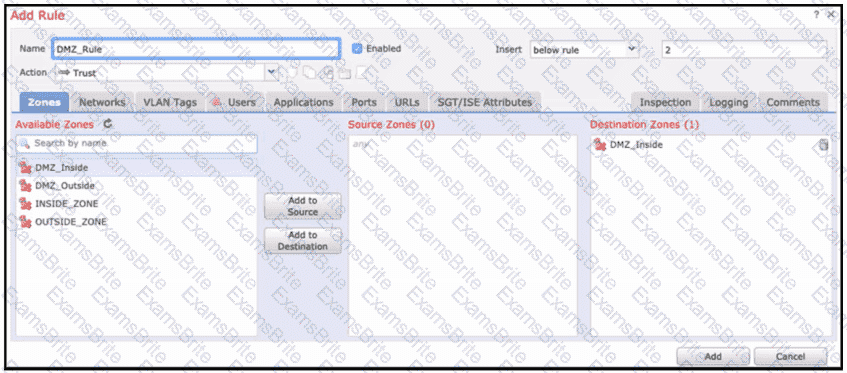
Refer to the exhibit. When configuring this access control rule in Cisco FMC, what happens with the traffic destined to the DMZ_inside zone once the configuration is deployed?
A network security engineer must export packet captures from the Cisco FMC web browser while troubleshooting an issue. When navigating to the address https:// < FMC IP > /capure/CAPI/pcap/test.pcap, an error 403: Forbidden is given instead of the PCAP file. Which action must the engineer take to resolve this issue?
Which feature requires a network discovery policy on the Cisco Firepower Next Generation Intrusion Prevention
System?
An engineer needs behavioral analysis to detect malicious activity on the hosts, and is configuring the
organization’s public cloud to send telemetry using the cloud provider’s mechanisms to a security device. Which
mechanism should the engineer configure to accomplish this goal?
Which type of data does the Cisco Stealthwatch system collect and analyze from routers, switches, and firewalls?
Which policy does a Cisco Secure Web Appliance use to block or monitor URL requests based on the reputation score?
Which interface mode does a Cisco Secure IPS device use to block suspicious traffic?
An organization is implementing AAA for their users. They need to ensure that authorization is verified for every command that is being entered by the network administrator. Which protocol must be configured in order to provide this capability?
What is the term for having information about threats and threat actors that helps mitigate harmful events that would otherwise compromise networks or systems?
An engineer must deploy a Cisco Secure Web Appliance. Antimalware scanning must use the Outbreak Heuristics antimalware category on files identified as malware before performing any other processes. What must be configured on the Secure Web Appliance to meet the requirements?
Which PKI enrollment method allows the user to separate authentication and enrollment actions and also
provides an option to specify HTTP/TFTP commands to perform file retrieval from the server?
A network engineer is configuring a Cisco Catalyst switch. The network engineer must prevent traffic on the network from being interrupted by broadcast packets flooding the network using a predefined threshold. What must be configured on the switch?
When network telemetry is implemented, what is important to be enabled across all network infrastructure devices to correlate different sources?
An engineer is configuring IPsec VPN and needs an authentication protocol that is reliable and supports ACK
and sequence. Which protocol accomplishes this goal?
A network engineer must distribute an operating system image to a network device and activate the image on that device by using the Cisco Catalyst Center API. Which two API requests perform the required operations? (Choose two.)
Which two methods are available in Cisco Secure Web Appliance to process client requests when configured in Transparent mode? (Choose two.)
An engineer is configuring web filtering for a network using Cisco Umbrella Secure Internet Gateway.
The requirement is that all traffic needs to be filtered. Using the SSL decryption feature, which type of
certificate should be presented to the end-user to accomplish this goal?
A network administrator needs a solution to match traffic and allow or deny the traffic based on the type of application, not just the source or destination address and port used. Which kind of security product must the network administrator implement to meet this requirement?
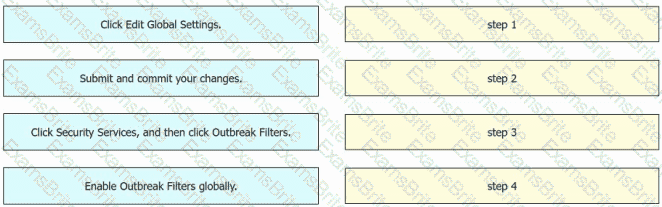
An engineer must enable Outbreak Filters globally on an AsyncOS for Cisco Secure Email Gateway to protect the network from large-scale malware attacks. Drag and drop the steps from the left into the sequence on the right to complete the configuration.
In which two customer environments is the Cisco Secure Web Appliance Virtual connector traffic direction method selected? (Choose two.)
Which type of DNS abuse exchanges data between two computers even when there is no direct connection?
Which Cisco Advanced Malware protection for Endpoints deployment architecture is designed to keep data
within a network perimeter?
An organization wants to implement a cloud-delivered and SaaS-based solution to provide visibility and threat detection across the AWS network. The solution must be deployed without software agents and rely on AWS VPC flow logs instead. Which solution meets these requirements?
Which action configures the IEEE 802.1X Flexible Authentication feature to support Layer 3 authentication mechanisms?
An organization wants to use Cisco FTD or Cisco ASA devices. Specific URLs must be blocked from being
accessed via the firewall which requires that the administrator input the bad URL categories that the
organization wants blocked into the access policy. Which solution should be used to meet this requirement?
A security engineer is tasked with configuring TACACS on a Cisco ASA firewall. The engineer must be able to access the firewall command line interface remotely. The authentication must fall back to the local user database of the Cisco ASA firewall. AAA server group named TACACS-GROUP is already configured with TACACS server IP address 192.168.10.10 and key C1sc0512222832!. Which configuration must be done next to meet the requirement?
Which API method and required attribute are used to add a device into Cisco DNA Center with the native API?
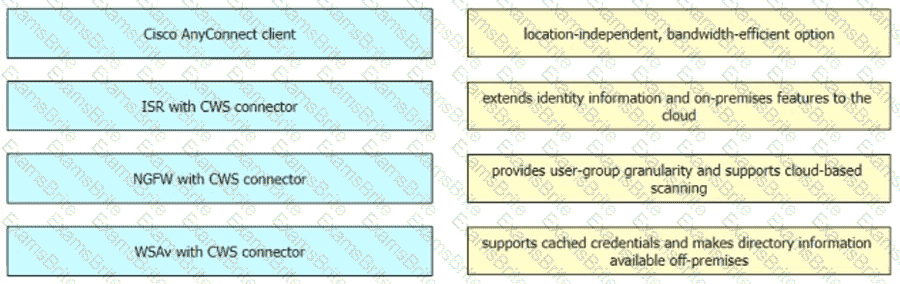
Drag and drop the Cisco CWS redirection options from the left onto the capabilities on the right.
An engineer must configure Cisco AMP for Endpoints so that it contains a list of files that should not be executed by users. These files must not be quarantined. Which action meets this configuration requirement?
An engineer has enabled LDAP accept queries on a listener. Malicious actors must be prevented from quickly
identifying all valid recipients. What must be done on the Cisco ESA to accomplish this goal?
A security engineer is deploying an IPsec site-to-site VPN between headquarters and a remote plant, protected by Cisco Secure Firewall Threat Defense managed by Cisco Secure Firewall Management Center. The following configurations have already been completed:
Matching IKEv2 proposals, preshared keys, and IPsec transform sets
Access control rules permitting the traffic
Crypto maps applied to the outside interfaces
VPN traffic exempted from inspection
During a packet capture on the firewall, the engineer observes that the traffic is translated to the public IP address, preventing tunnel establishment. Which configuration action must be performed next?
An administrator is configuring N I P on Cisco ASA via ASDM and needs to ensure that rogue NTP servers cannot insert themselves as the authoritative time source Which two steps must be taken to accomplish this task? (Choose two)
Which two solutions help combat social engineering and phishing at the endpoint level? (Choose two.)
In which two ways does Easy Connect help control network access when used with Cisco TrustSec? (Choose two)
Which action must be taken in the AMP for Endpoints console to detect specific MD5 signatures on endpoints and then quarantine the files?
What is a key feature of the Bring Your Own Device (BYOD) capability in Cisco ISE?
Which technology provides the benefit of Layer 3 through Layer 7 innovative deep packet inspection,
enabling the platform to identify and output various applications within the network traffic flows?
An engineer must force an endpoint to re-authenticate an already authenticated session without disrupting the
endpoint to apply a new or updated policy from ISE. Which CoA type achieves this goal?
Which portion of the network do EPP solutions solely focus on and EDR solutions do not?
A security test performed on one of the applications shows that user input is not validated. Which security vulnerability is the application more susceptible to because of this lack of validation?
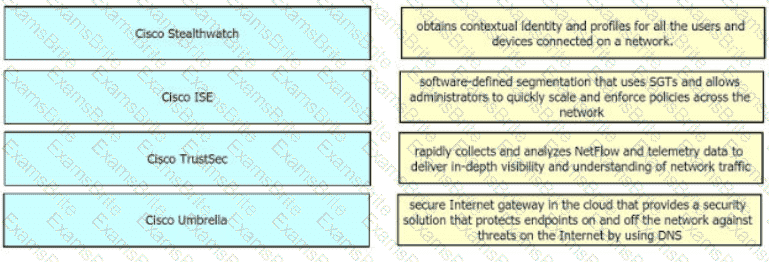
Drag and drop the solutions from the left onto the solution ' s benefits on the right.
An organization is trying to implement micro-segmentation on the network and wants to be able to gain visibility on the applications within the network. The solution must be able to maintain and force compliance. Which product should be used to meet these requirements?
Which feature within Cisco Umbrella allows for the ability to inspect secure HTTP traffic?
What is the recommendation in a zero-trust model before granting access to corporate applications and resources?
Which two actions does the Cisco ISE posture module provide that ensures endpoint security? (Choose two.)
Which Cisco platform onboards the endpoint and can issue a CA signed certificate while also automatically configuring endpoint network settings to use the signed endpoint certificate, allowing the endpoint to gain network access?
When wired 802.1X authentication is implemented, which two components are required? (Choose two)
What is the term for when an endpoint is associated to a provisioning WLAN that is shared with guest
access, and the same guest portal is used as the BYOD portal?
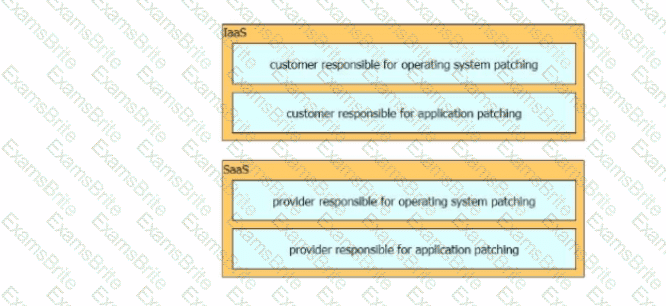
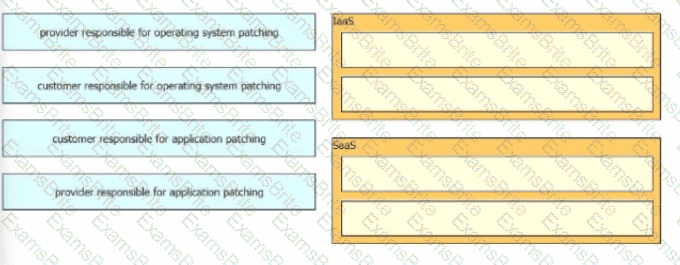
Drag and drop the security responsibilities from the left onto the corresponding cloud service models on the right.
An engineer is configuring Cisco Secure Endpoint to enhance security by preventing the execution of certain files by users. The engineer needs to ensure that the specific executable file name Cisco_Software_0505446151.exe is blocked from running while never being quarantined. What must the engineer configure to meet the requirement?
What is a benefit of a Cisco Secure Email Gateway Virtual as compared to a physical Secure Email Gateway?
What can be integrated with Cisco Threat Intelligence Director to provide information about security threats,
which allows the SOC to proactively automate responses to those threats?
Which characteristic is unique to a Cisco WSAv as compared to a physical appliance?
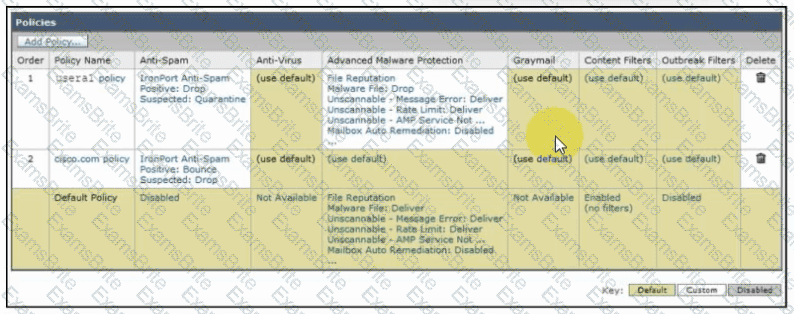
Refer to the exhibit. An engineer must configure an incoming mail policy so that each email sent from usera1@example.com to a domain of @cisco.com is scanned for antispam and advanced malware protection. All other settings will use the default behavior. What must be configured in the incoming mail policy to meet the requirements?
An engineer is configuring Cisco WSA and needs to enable a separated email transfer flow from the Internet and from the LAN. Which deployment mode must be used to accomplish this goal?
A network engineer is deciding whether to use stateful or stateless failover when configuring two Cisco ASAs for high availability. What is the connection status in both cases?
Refer to the exhibit.
=== Cisco Secure Endpoint - Detection Event ===
Endpoint : LAB-WKSTN-047 User: user1
Policy Group : Lab-Workstations Mode: Audit
Engine : ETHOS (fuzzy fingerprint)
Disposition : Malicious
File : C:\Users\user1\AppData\Local\Temp\svchost32.exe
SHA256 : 3a9f2c1d...e881b4a7
Parent Process: winword.exe
Threat Name : W32.Trojan.GenericKD.Agent
Retrospective : Previously UNKNOWN
Disposition changed to MALICIOUS at 09:31:55 UTC
File Activity : Created, Executed
Network : TCP outbound - > 91.205.188.47:4444
DNS query: c2-update.pharmadomain.ru
Quarantine : NOT quarantined (Audit mode active)
A security analyst at a pharmaceutical company is reviewing a Cisco Secure Endpoint malware-detection alert triggered on a laboratory workstation. The analyst observes the event data above. Which two things are occurring? (Choose two.)
Which cloud service model offers an environment for cloud consumers to develop and deploy applications
without needing to manage or maintain the underlying cloud infrastructure?
Which type of API is being used when a security application notifies a controller within a software-defined network architecture about a specific security threat?
Which Cisco Umbrella package supports selective proxy for Inspection of traffic from risky domains?
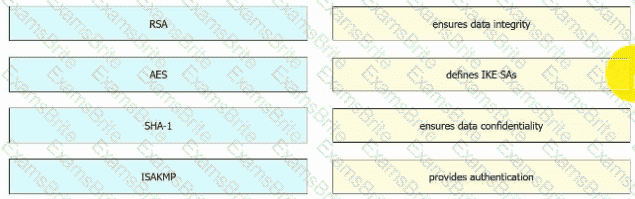
Drag and drop the VPN functions from the left onto the descriptions on the right.
A network engineer is deploying multiple Cisco Secure Firewall Threat Defense devices across two data centers. The solution has the following requirements:
Management must have no Internet dependency.
Management must remain accessible during major outages.
Policy management must be centralized.
Which solution must be implemented to meet the requirements?
Which algorithm provides encryption and authentication for data plane communication?
An organization has DHCP servers set up to allocate IP addresses to clients on the LAN. What must be done to ensure the LAN switches prevent malicious DHCP traffic while also distributing IP addresses to the correct endpoints?
Which Cisco DNA Center Intent API action is used to retrieve the number of devices known to a DNA Center?
What is a required prerequisite to enable malware file scanning for the Secure Internet Gateway?
A user has a device in the network that is receiving too many connection requests from multiple machines.
Which type of attack is the device undergoing?
For Cisco IOS PKI, which two types of Servers are used as a distribution point for CRLs? (Choose two)
What is the default action before identifying the URL during HTTPS inspection in Cisco Secure Firewall Threat Defense software?
What is the primary difference between an Endpoint Protection Platform and an Endpoint Detection and
Response?
An organization wants to secure data in a cloud environment. Its security model requires that all users be
authenticated and authorized. Security configuration and posture must be continuously validated before access is granted or maintained to applications and data. There is also a need to allow certain application traffic and deny all other traffic by default. Which technology must be used to implement these requirements?
An engineer is trying to decide between using L2TP or GRE over IPsec for their site-to-site VPN implementation. What must be un solution?
A security policy administrator configures a Cisco Secure Access SIA DNS policy to block all social media categories for the Marketing Active Directory group. While testing from one of the user machines, access to the domain https://socialmediaexample.org is allowed. When searching for this domain in User Activity Search, no queries for that specific domain are returned. Consider these facts:
The test user is part of the Marketing Active Directory group.
The domain socialmediaexample.org belongs to the social media category.
The user is configured with the Umbrella Roaming Client for DNS redirection.
All other social media websites are properly blocked for the same user and match the correct policy.
Which configuration must the administrator implement in Cisco Secure Access to meet the requirement?
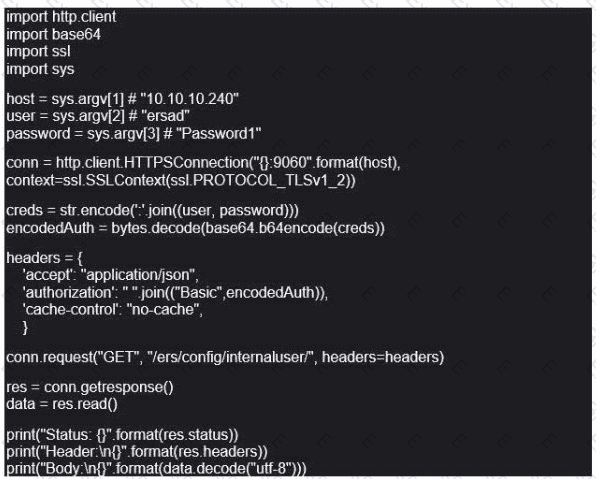
Refer to the exhibit.
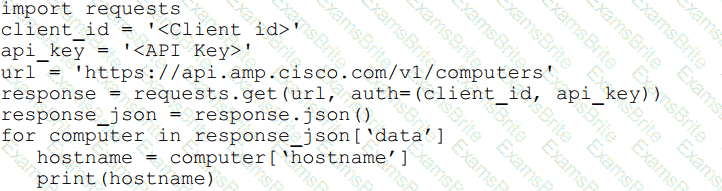
What will happen when the Python script is executed?
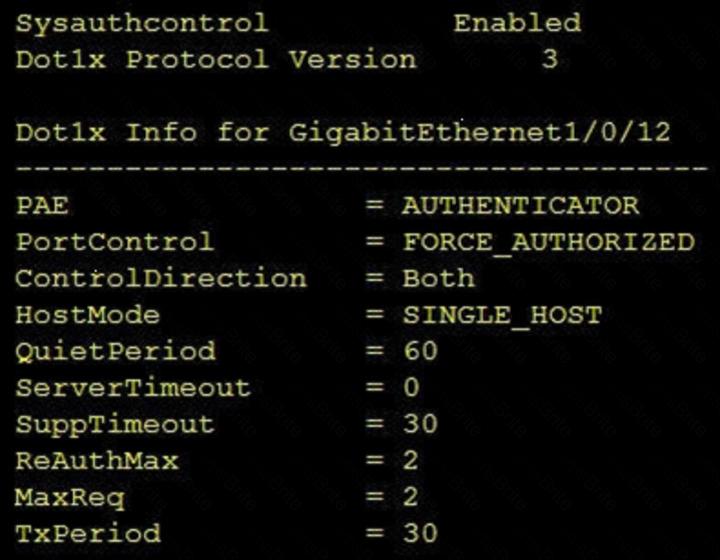
Refer to the exhibit,
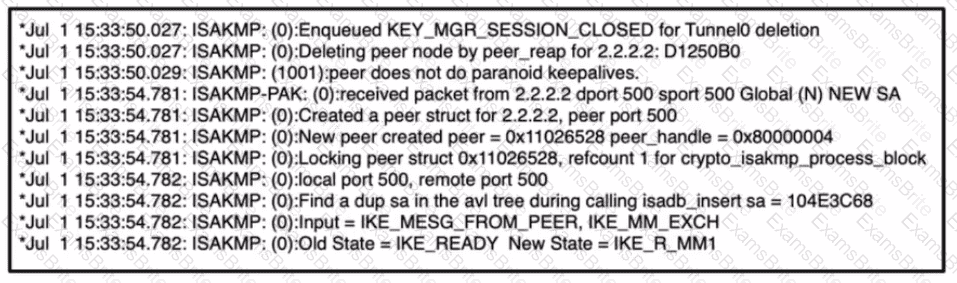
which command results in these messages when attempting to troubleshoot an iPsec VPN connection?
Which risk is created when using an Internet browser to access cloud-based service?
An attacker needs to perform reconnaissance on a target system to help gain access to it. The system has weak passwords, no encryption on the VPN links, and software bugs on the system’s applications. Which
vulnerability allows the attacker to see the passwords being transmitted in clear text?
An engineer adds a custom detection policy to a Cisco AMP deployment and encounters issues with the
configuration. The simple detection mechanism is configured, but the dashboard indicates that the hash is not 64 characters and is non-zero. What is the issue?
A Cisco Secure Cloud Analytics administrator is setting up a private network monitor sensor to monitor an on-premises environment. Which two pieces of information from the sensor are used to link to the Secure Cloud Analytics portal? (Choose two.)
A company has 5000 Windows users on its campus. Which two precautions should IT take to prevent WannaCry ransomware from spreading to all clients? (Choose two.)
What is the result of the ACME-Router(config)#login block-for 100 attempts 4 within 60 command on a Cisco IOS router?
Which VMware platform does Cisco ACI integrate with to provide enhanced visibility, provide policy integration and deployment, and implement security policies with access lists?
A Cisco ESA network administrator has been tasked to use a newly installed service to help create policy based on the reputation verdict. During testing, it is discovered that the Cisco ESA is not dropping files that have an undetermined verdict. What is causing this issue?
Email security has become a high-priority task for a security engineer at a large multi-national organization due to ongoing phishing campaigns. To help control this, the engineer has deployed an Incoming Content Filter with a URL reputation of (-10.00 to -6.00) on the Cisco Secure Email Gateway. Which action will the system perform to disable any links in messages that match the filter?
Which Cisco solution does Cisco Umbrella integrate with to determine if a URL is malicious?
After deploying a Cisco ESA on your network, you notice that some messages fail to reach their destinations.
Which task can you perform to determine where each message was lost?
Which two features of Cisco Email Security can protect your organization against email threats? (Choose two)
An administrator enables Cisco Threat Intelligence Director on a Cisco FMC. Which process uses STIX and allows uploads and downloads of block lists?
After a recent breach, an organization determined that phishing was used to gain initial access to the network before regaining persistence. The information gained from the phishing attack was a result of users visiting known malicious websites. What must be done in order to prevent this from happening in the future?
Which two activities are performed using Cisco Catalyst Center? (Choose two.)
Which Cisco platform processes behavior baselines, monitors for deviations, and reviews for malicious processes in data center traffic and servers while performing software vulnerability detection?
A security engineer requires social-media websites to be blocked through Cisco Secure Firewall Threat Defense. Which configuration action must the engineer apply to meet the requirement?
Which Cisco security solution determines if an endpoint has the latest OS updates and patches installed on the system?
With Cisco AMP for Endpoints, which option shows a list of all files that have been executed in your
environment?
What are two advantages of using Cisco Any connect over DMVPN? (Choose two)
Which two statements about a Cisco WSA configured in Transparent mode are true? (Choose two)
Which kind of API that is used with Cisco DNA Center provisions SSIDs, QoS policies, and update software versions on switches?
What Cisco command shows you the status of an 802.1X connection on interface gi0/1?
What are two benefits of using Cisco Duo as an MFA solution? (Choose two.)
An engineer is securing access to data served by a cloud-based application. The data must be protected from modification in transit, and its integrity must be validated. The following security measures have been implemented:
• Governance with role-based access control based on the principle of least privilege
• TLS 1.3 with signed certificates
• AES-256 with MD5
What must be configured to complete the secure implementation?
An engineer enabled SSL decryption for Cisco Umbrella intelligent proxy and needs to ensure that traffic is inspected without alerting end-users. Which action accomplishes this goal?
Which capability allows an administrator to configure forensics rules in Cisco Secure Workload?
Based on the NIST 800-145 guide, which cloud architecture may be owned, managed, and operated by one or more of the organizations in the community, a third party, or some combination of them, and it may exist on or off premises?
Refer to the exhibit.
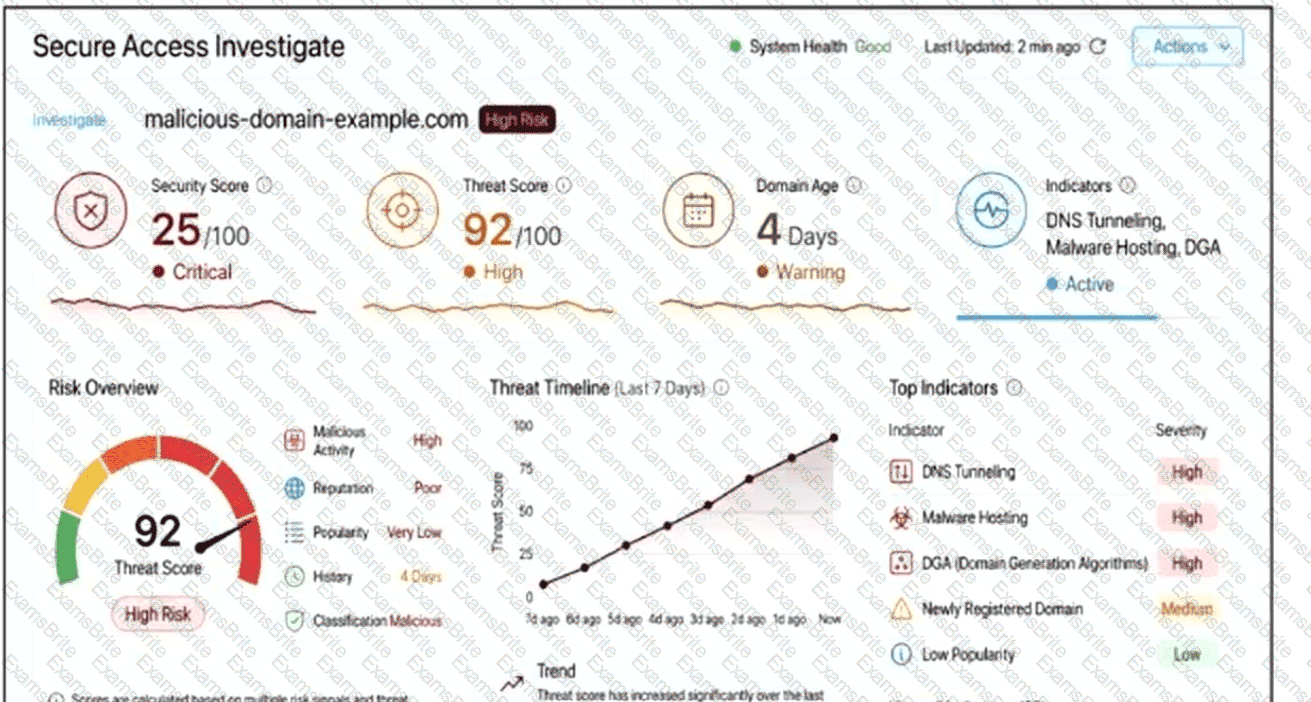
What conclusion should an administrator draw about the URL malicious-domain-example.com?
What are two characteristics of the RESTful architecture used within Cisco DNA Center? (Choose two.)
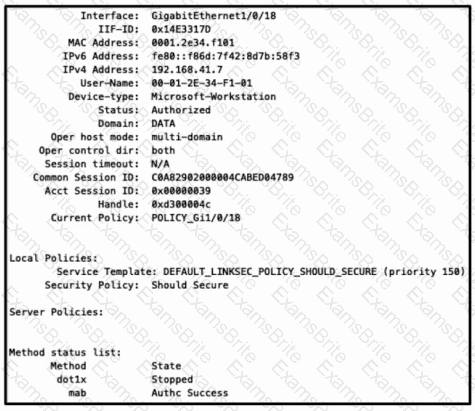
Refer to the exhibit. Which configuration item makes it possible to have the AAA session on the network?
Which product allows Cisco FMC to push security intelligence observable to its sensors from other products?
Which security control is required for identifying and neutralizing malicious code that attempts to execute on an endpoint?
What are two ways that Cisco Container Platform provides value to customers who utilize cloud service providers? (Choose two.)
When a Cisco Secure Web Appliance checks a web request, what occurs if it is unable to match a user-defined policy?
What are two reasons for implementing a multifactor authentication solution such as Duo Security provide to an
organization? (Choose two)
Which type of dashboard does Cisco DNA Center provide for complete control of the network?
Which Cisco DNA Center RESTful PNP API adds and claims a device into a workflow?
Which two protocols must be configured to authenticate end users to the Cisco WSA? (Choose two.)
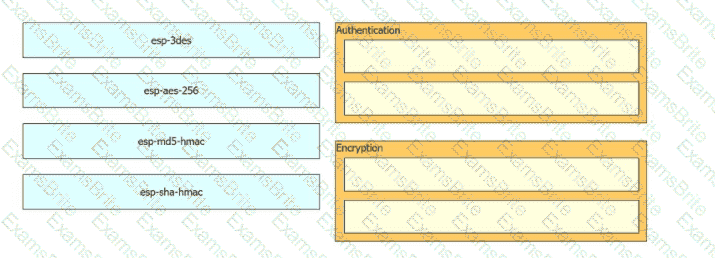
Drag and drop the cryptographic algorithms for IPsec from the left onto the cryptographic processes on the right.
A security engineer is deploying an IPsec site-to-site VPN between headquarters and a remote plant, protected by Cisco Secure Firewall Threat Defense managed by Cisco Secure Firewall Management Center. The following configurations have already been completed:
Matching IKEv2 proposals, preshared keys, and IPsec transform sets
Access control rules permitting the traffic
Crypto maps applied to the outside interfaces
VPN traffic exempted from inspection
During a packet capture on the firewall, the engineer observes that the traffic is translated to the public IP address, preventing tunnel establishment. Which configuration action must be performed next?
An engineer needs to configure a Cisco Secure Email Gateway (SEG) to prompt users to enter multiple forms of identification before gaining access to the SEG. The SEG must also join a cluster using the preshared key of cisc421555367. What steps must be taken to support this?
Which feature is used in a push model to allow for session identification, host reauthentication, and session termination?
An engineer is implementing NTP authentication within their network and has configured both the client and server devices with the command ntp authentication-key 1 md5 Cisc392368270. The server at 1.1.1.1 is attempting to authenticate to the client at 1.1.1.2, however it is unable to do so. Which command is required to enable the client to accept the server’s authentication key?
A Cisco AMP for Endpoints administrator configures a custom detection policy to add specific MD5 signatures The configuration is created in the simple detection policy section, but it does not work What is the reason for this failure?
Which two functions does the Cisco Advanced Phishing Protection solution perform in trying to protect from phishing attacks? (Choose two.)
A network administrator is configuring a switch to use Cisco ISE for 802.1X. An endpoint is failing
authentication and is unable to access the network. Where should the administrator begin troubleshooting to verify the authentication details?
Which action configures the IEEE 802.1X Flexible Authentication feature lo support Layer 3 authentication mechanisms?
A security engineer must protect endpoints when a file appears harmless during initial inspection but later shows malicious behavior. The solution must continuously observe process and file activity after execution and respond when a threat emerges. The infrastructure includes Cisco Secure Endpoint. Which feature must the engineer configure to meet the requirements?
A network engineer has entered the snmp-server user andy myv3 auth sha cisco priv aes 256
cisc0380739941 command and needs to send SNMP information to a host at 10.255.254.1. Which command achieves this goal?
Which Splunk SOAR component automates multi-step security actions into a repeatable workflow?
When a Cisco WSA checks a web request, what occurs if it is unable to match a user-defined policy?
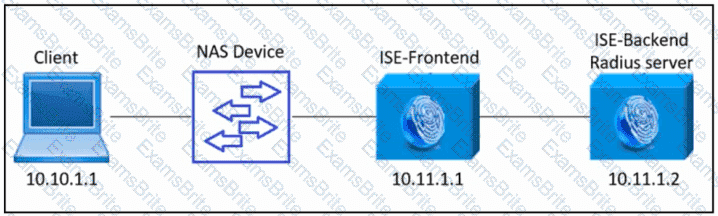
Refer to the exhibit. An engineer must configure a new Cisco ISE backend server as a RADIUS server to provide AAA for all access requests from the client to the ISE-Frontend server.
Which Cisco ISE configuration must be used?
Which two kinds of attacks are prevented by multifactor authentication? (Choose two)
Which solution offers automated blocking of known threats and visibility into zero-day attack behavior, with the ability to respond directly from the console?
What are the two types of managed Intercloud Fabric deployment models? (Choose two.)
What is a functional difference between Cisco AMP for Endpoints and Cisco Umbrella Roaming Client?
Which suspicious pattern enables the Cisco Tetration platform to learn the normal behavior of users?
Refer to the exhibit.
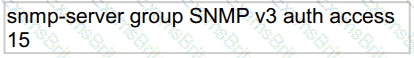
What does the number 15 represent in this configuration?
Refer to the exhibit.
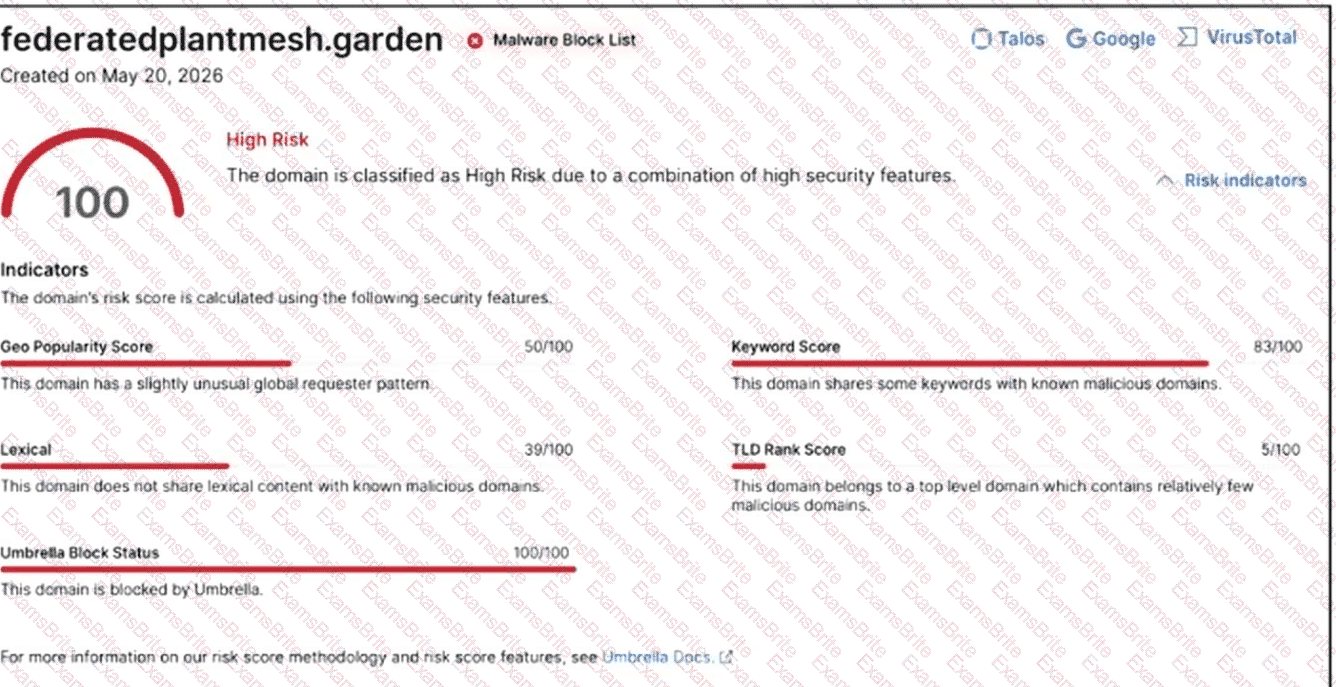
A threat analyst is investigating the domain federatedplantmesh.garden after it appeared in DNS logs from several roaming users. In the Cisco Secure Access Investigate dashboard, the analyst notes that several individual indicators, including Lexical, TLD, and Geo Popularity, are not strongly elevated, yet the overall Risk Score is 100. What is occurring?
What are two facts about WSA HTTP proxy configuration with a PAC file? (Choose two.)
An engineer must implement a file transfer solution between a company ' s data center and branches. The company has numerous servers hosted in a hybrid cloud implementation. The file transfer protocol must support authentication, protect the data against unauthorized access, and ensure that users cannot list directories or remove files remotely. Which protocol must be used?
A network administrator is modifying a remote access VPN on an FTD managed by an FMC. The administrator wants to offload traffic to certain trusted domains. The administrator wants this traffic to go out of the client ' s local internet and send other internet-bound traffic over the VPN Which feature must the administrator configure?
A company identified a phishing vulnerability during a pentest. What are two ways the company can protect employees from the attack? (Choose two.)
A network engineer must monitor user and device behavior within the on-premises network. This data must be sent to the Cisco Stealthwatch Cloud analytics platform for analysis. What must be done to meet this
requirement using the Ubuntu-based VM appliance deployed in a VMware-based hypervisor?
Which Talos reputation center allows for tracking the reputation of IP addresses for email and web traffic?
Which two components do southbound APIs use to communicate with downstream devices? (Choose two.)
Refer to the exhibit.
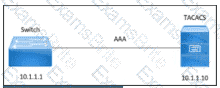
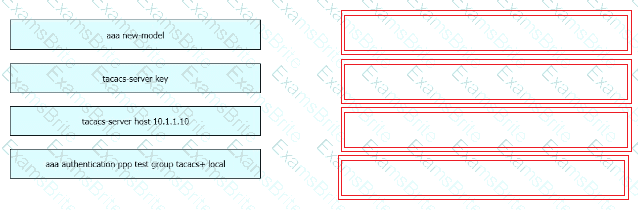
An engineer must configure a Cisco switch to perform PPP authentication via a TACACS server located at IP address 10.1.1.10. Authentication must fall back to the local database using the username LocalUser and password C1Sc0451069341l if the TACACS server is unreachable.
Drag and drop the commands from the left onto the corresponding configuration steps on the right.
Which solution combines Cisco IOS and IOS XE components to enable administrators to recognize
applications, collect and send network metrics to Cisco Prime and other third-party management tools, and prioritize application traffic?
Which Cisco ASA Platform mode disables the threat detection features except for Advanced Threat Statistics?
What are two characteristics of Cisco Catalyst Center APIs? (Choose two.)
Which two authentication protocols are supported by the Cisco WSA? (Choose two.)
Which posture assessment requirement provides options to the client for remediation and requires the
remediation within a certain timeframe?
Which two global commands must the network administrator implement to limit the attack surface of an internet-facing Cisco router? (Choose two.)
A network engineer is trying to figure out whether FlexVPN or DMVPN would fit better in their environment.
They have a requirement for more stringent security multiple security associations for the connections, more efficient VPN establishment as well consuming less bandwidth. Which solution would be best for this and why?
An engineer is deploying a Cisco Secure Email Gateway and must ensure it reaches the Cisco update servers to retrieve new rules. The engineer must now manually configure the Outbreak Filter rules on an AsyncOS for Cisco Secure Email Gateway. Only outdated rules must be replaced. Up-to-date rules must be retained. Which action must the engineer take next to complete the configuration?
Which telemetry data captures variations seen within the flow, such as the packets TTL, IP/TCP flags, and payload length?
Refer to the exhibit.
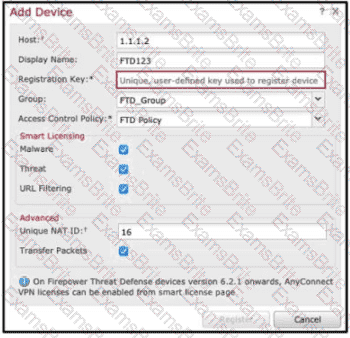
An administrator is adding a new Cisco FTD device to their network and wants to manage it with Cisco FMC.
The Cisco FTD is not behind a NAT device. Which command is needed to enable this on the Cisco FTD?
An organization deploys multiple Cisco FTD appliances and wants to manage them using one centralized
solution. The organization does not have a local VM but does have existing Cisco ASAs that must migrate over
to Cisco FTDs. Which solution meets the needs of the organization?
In which cloud services model is the customer responsible for scanning for and mitigation of application vulnerabilities?
Which solution is made from a collection of secure development practices and guidelines that developers must follow to build secure applications?
Which solution for remote workers enables protection, detection, and response on the endpoint against known and unknown threats?
An administrator is adding a new switch onto the network and has configured AAA for network access control. When testing the configuration, the RADIUS authenticates to Cisco ISE but is being rejected. Why is the ip radius source-interface command needed for this configuration?
Which ASA deployment mode can provide separation of management on a shared appliance?
Which deployment model is the most secure when considering risks to cloud adoption?
How many interfaces per bridge group does an ASA bridge group deployment support?
Which benefit does endpoint security provide the overall security posture of an organization?
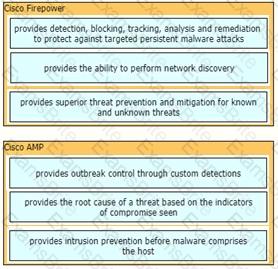
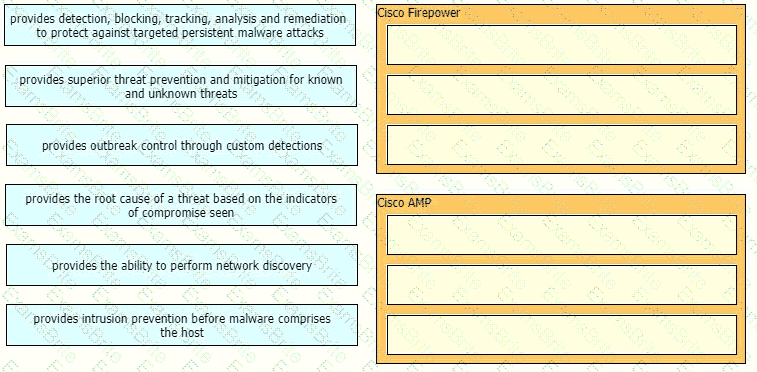
Drag and drop the capabilities of Cisco Firepower versus Cisco AMP from the left into the appropriate category on the right.
During a recent security audit a Cisco IOS router with a working IPSEC configuration using IKEv1 was flagged for using a wildcard mask with the crypto isakmp key command The VPN peer is a SOHO router with a dynamically assigned IP address Dynamic DNS has been configured on the SOHO router to map the dynamic IP address to the host name of vpn sohoroutercompany.com In addition to the command crypto isakmp key Cisc425007536 hostname vpn.sohoroutercompany.com what other two commands are now required on the Cisco IOS router for the VPN to continue to function after the wildcard command is removed? (Choose two)
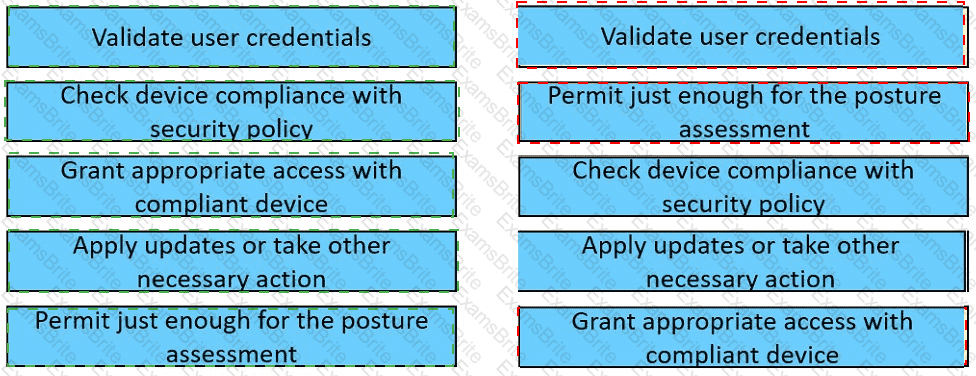
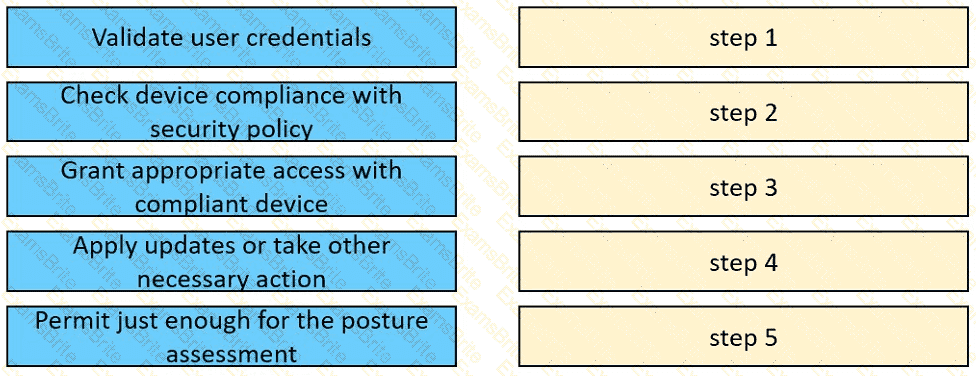
Drag and drop the posture assessment flow actions from the left into a sequence on the right.
Which statement about the configuration of Cisco ASA NetFlow v9 Secure Event Logging is true?
Which two application layer preprocessors are used by Firepower Next Generation Intrusion Prevention
System? (Choose two)
With which components does a southbound API within a software-defined network architecture communicate?
Which component of Cisco umbrella architecture increases reliability of the service?
How does Cisco Umbrella protect clients when they operate outside of the corporate network?
An engineer is configuring Cisco Secure Endpoint to enhance network security by specifying a large set of external IP addresses that must be monitored for potential threats. The engineer is configuring an IP List and must add the IP addresses to the list. Which configuration action must the engineer take next to meet the requirement?
Refer to the exhibit. A network engineer must configure a Cisco router to send traps using SNMPv3. The engineer configures a remote user to receive traps and sets the security level to use authentication without privacy. Which command completes the configuration?
How does Cisco Workload Optimization portion of the network do EPP solutions solely performance issues?
What is the purpose of threat intelligence in the Cisco Security Reference Architecture?
What is a prerequisite when integrating a Cisco ISE server and an AD domain?
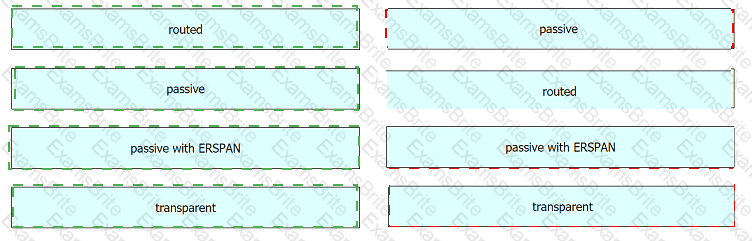
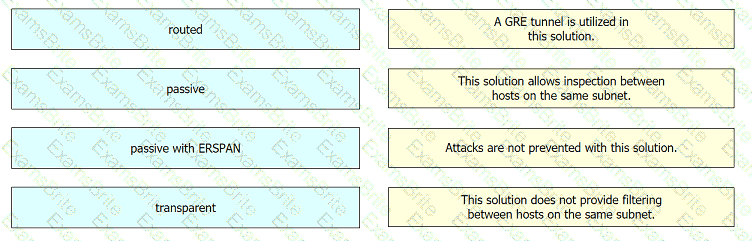
Drag and drop the deployment models from the left onto the explanations on the right.
Which open source tool does Cisco use to create graphical visualizations of network telemetry on Cisco IOS XE devices?
A network administrator needs to find out what assets currently exist on the network. Third-party systems need to be able to feed host data into Cisco Firepower. What must be configured to accomplish this?
What is a language format designed to exchange threat intelligence that can be transported over the TAXII
protocol?
Refer to the exhibit.
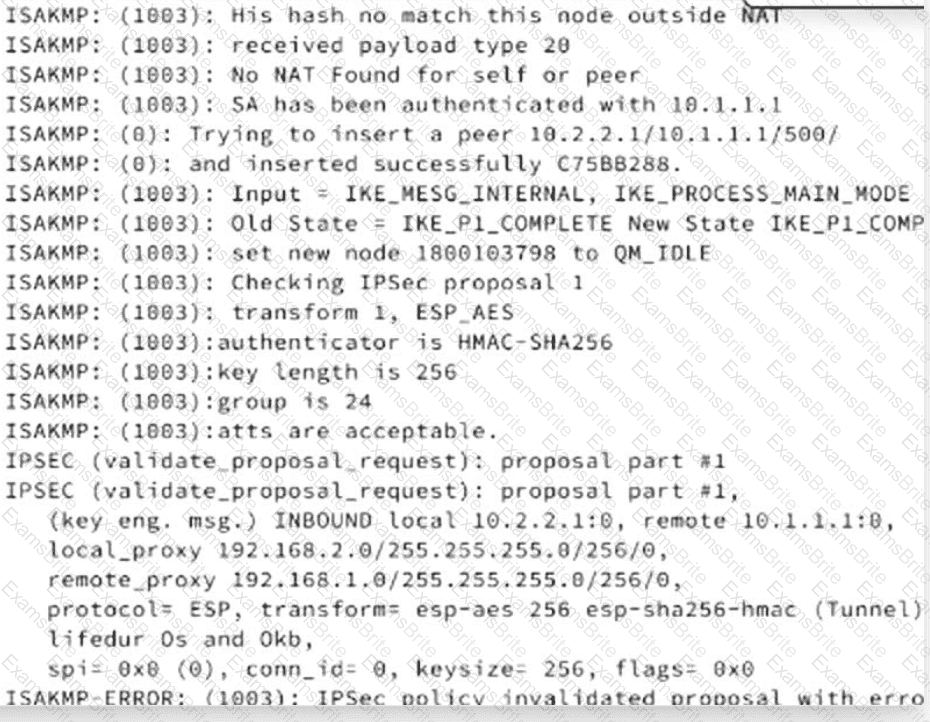
An engineer configures an IPsec VPN between two Cisco Secure Firewall Threat Defense devices named FTD1 and FTD2. However, the hosts behind FTD1 and FTD2 cannot communicate with each other. The engineer runs a debug command to troubleshoot the issue. What must be configured to resolve the issue?
An organization is receiving SPAM emails from a known malicious domain. What must be configured in order to
prevent the session during the initial TCP communication?
An engineer has been tasked with implementing a solution that can be leveraged for securing the cloud users,
data, and applications. There is a requirement to use the Cisco cloud native CASB and cloud cybersecurity
platform. What should be used to meet these requirements?
TESTED 16 Sep 2026