Weekend Sale Special 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

ExamsBrite Dumps

Security, Specialist (JNCIS-SEC) Question and Answers

Security, Specialist (JNCIS-SEC)

Last Update Sep 20, 2026
Total Questions : 68

We are offering FREE JN0-336 Juniper exam questions. All you do is to just go and sign up. Give your details, prepare JN0-336 free exam questions and then go for complete pool of Security, Specialist (JNCIS-SEC) test questions that will help you more.
JN0-336 pdf

JN0-336 PDF

$26.25  $104.99
JN0-336 Engine

JN0-336 Testing Engine

$31.25  $124.99
JN0-336 PDF + Engine

JN0-336 PDF + Testing Engine

$41.25  $164.99
Questions 1

You are deploying a new SRX Series device and you need to log denied traffic.

In this scenario, which two policy parameters are required to accomplish this task? (Choose two.)

Options:

A.  

session-init

B.  

session-close

C.  

deny

D.  

count

Discussion 0
Questions 2

Which two statements are correct about redundant fabric interfaces in a chassis cluster? (Choose two.)

Options:

A.  

fab0 and fab1 are located on both node0 and node1.

B.  

fab0 is located on node0, whereas fab1 is located on node1.

C.  

The media type must be the same for each redundant fabric interface.

D.  

The media type can be different for each redundant fabric interface.

Discussion 0
Questions 3

Which three different objects would be created, modified, cloned, and deleted in the Shared Objects workspace of Junos Space Security Director? (Choose three.)

Options:

A.  

geo IP

B.  

IP address

C.  

audit logs

D.  

policy enforcement groups

E.  

policy rules

Discussion 0
Questions 4

How does the SSL proxy detect if a particular session is SSL encrypted?

Options:

A.  

It uses AppID services.

B.  

It verifies the length of the packet.

C.  

It looks at the destination port number.

D.  

It uses a certificate authority (CA).

Discussion 0
Questions 5

Which two statements are correct about a chassis cluster? (Choose two.)

Options:

A.  

If the cluster ID is set to 0, the HA configuration is ignored.

B.  

You must reboot the device anytime you change the node ID configuration.

C.  

If the node ID is set to 0, the HA configuration is ignored.

D.  

You must have multiple Layer 2 domains if you require more than 255 node IDs.

Discussion 0
Questions 6

You want to include a custom attack object named Custom-FTP-Attack and set the action to drop the packet.
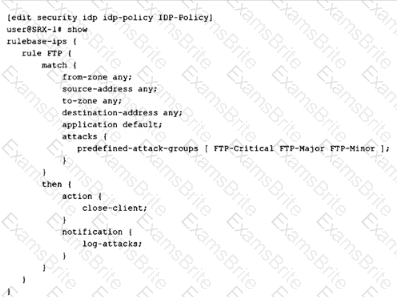
Referring to the exhibit, which modifications would you make?

Options:

A.  

Add custom-attack Custom-FTP-Attack to the attacks section and change the action to close-client.

B.  

Add custom-attack Custom-FTP-Attack to the attacks section and change the action to drop-packet.

C.  

Add custom-attack Custom-FTP-Attack to the action section and change the action to drop-packet.

D.  

Add custom-attack Custom-FTP-Attack to the notification section and change the action to drop-packet.

Discussion 0
Questions 7

You are implementing an SRX Series device at a branch office that has low bandwidth and also uses a cloud-based VoIP solution with an outbound policy that permits all traffic.

Which service would you implement at your edge device to prioritize VoIP traffic in this scenario?

Options:

A.  

AppFW

B.  

SIP ALG

C.  

AppQoE

D.  

AppQoS

Discussion 0
Questions 8

You need to set up a forward proxy on your SRX Series device.

In this scenario, which two statements are correct? (Choose two.)

Options:

A.  

The forward proxy uses the managed SRX as a trusted certificate authority (CA).

B.  

The forward proxy forwards the server certificate.

C.  

The forward proxy looks like a client to the servers to which it communicates.

D.  

The forward proxy uses Encrypted Traffic Insights to monitor traffic.

Discussion 0
Questions 9

How does the SSL proxy service identify SSL traffic?

Options:

A.  

by examining the URL

B.  

by using AppID results

C.  

by examining the destination port

D.  

by reading the server certificate

Discussion 0
Questions 10

Which two steps are necessary to prepare the Active Directory domain for a JIMS installation? (Choose two.)

Options:

A.  

Create two limited access user accounts.

B.  

Create three limited access user accounts.

C.  

Add one full access user account to Active Directory groups.

D.  

Add limited access user accounts to Active Directory groups.

Discussion 0
Questions 11

Which two statements are correct about Juniper Secure Connect? (Choose two.)

Options:

A.  

Juniper Secure Connect uses a policy-based VPN.

B.  

Juniper Secure Connect can use a self-signed certificate.

C.  

Juniper Secure Connect uses a route-based VPN.

D.  

Juniper Secure Connect cannot use a self-signed certificate.

Discussion 0
Questions 12

What are two ways that Juniper Secure Connect provides flexibility in connection and authentication methods while ensuring that remote users are able to securely access company servers and cloud resources? (Choose two.)

Options:

A.  

It uses a persistent agent.

B.  

It uses Kerberos authentication.

C.  

It uses external authentication.

D.  

It uses an SSL VPN.

Discussion 0
Questions 13

You are asked to use Junos Space Security Director to download the latest application signatures in the AppID database.

In this scenario, which two statements are correct? (Choose two.)

Options:

A.  

The AppID database is stored in Junos Space Security Director.

B.  

The AppID database is stored on the managed SRX Series device.

C.  

The AppID database is maintained by a third-party host.

D.  

The AppID database is stored on a local storage server in the management network.

Discussion 0
Questions 14

What are two properties negotiated during IKE Phase 2? (Choose two.)

Options:

A.  

routing protocol

B.  

tunneling protocol

C.  

aggressive mode

D.  

Perfect Forward Secrecy

Discussion 0
Questions 15

In Juniper high availability (HA) SRX Series device implementations, which interface will be used to exchange session state, configuration files, and ensure session continuity across nodes using the proprietary Trivial Network Protocol?

Options:

A.  

fab

B.  

fxp0

C.  

fxp1

D.  

swfab

Discussion 0
Questions 16

Regarding static attack object groups, which two statements are true? (Choose two.)

Options:

A.  

Matching attack objects are automatically added to a custom group.

B.  

Group membership automatically changes when Juniper updates the IPS signature database.

C.  

Group membership does not automatically change when Juniper updates the IPS signature database.

D.  

You must manually add matching attack objects to a custom group.

Discussion 0
Questions 17

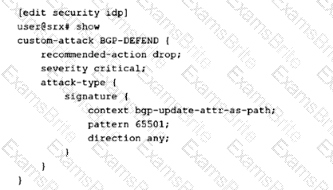
Which action will the SRX Series device take if traffic matches the custom attack object shown in the exhibit?
Options:

A.  

the action taken is defined in the IDP policy that includes this attack object.

B.  

the action taken is defined by the security policy.

C.  

The SRX Series device will reject the traffic.

D.  

The SRX series device will drop the traffic.

Discussion 0
Questions 18

Which protocol does the SRX Series Firewall use to communicate with a Windows domain controller?

Options:

A.  

SSH

B.  

LDAP

C.  

DNS

D.  

NETCONF

Discussion 0
Questions 19

An administrator decides to designate a node as the primary node for the chassis cluster.

Which statement is correct in this scenario?

Options:

A.  

Configure the burnt-in-address (BIA) to the highest value to bring the node as the primary node.

B.  

The node with the highest priority will become a primary node.

C.  

The node with the lowest priority will become a primary node.

D.  

Nodes with a priority of one are ineligible to participate in the election process.

Discussion 0
Questions 20

Which two statements are correct about Juniper ATP Cloud malware analysis? (Choose two.)
Options:

A.  

If no match exists in cache, the remaining analysis features are processed with the cumulative threat score transmitted to the SRX Series device.

B.  

If a match exists in cache, that threat score is sent to the SRX Series device and the analysis continues.

C.  

If a match exists in cache, that threat score is sent to the SRX Series device and the analysis stops.

D.  

If no match exists in cache, the first analysis feature to generate a threat score is transmitted to the SRX Series device.

Discussion 0