Developing in Agentic AI Systems
Last Update Sep 23, 2026
Total Questions : 106
We are offering FREE GH-600 Microsoft exam questions. All you do is to just go and sign up. Give your details, prepare GH-600 free exam questions and then go for complete pool of Developing in Agentic AI Systems test questions that will help you more.
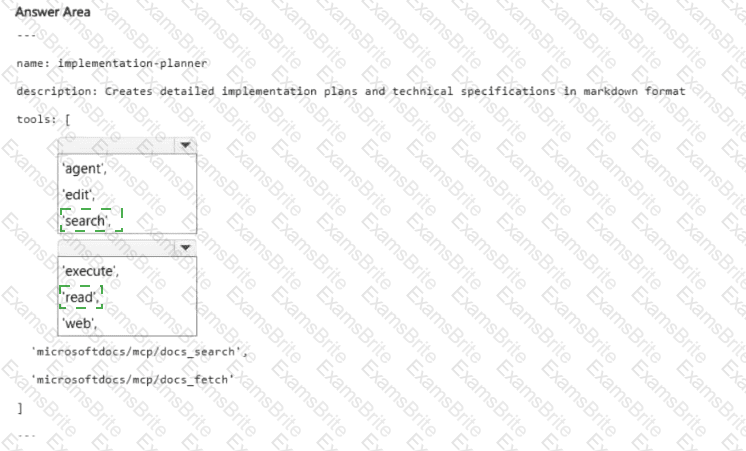
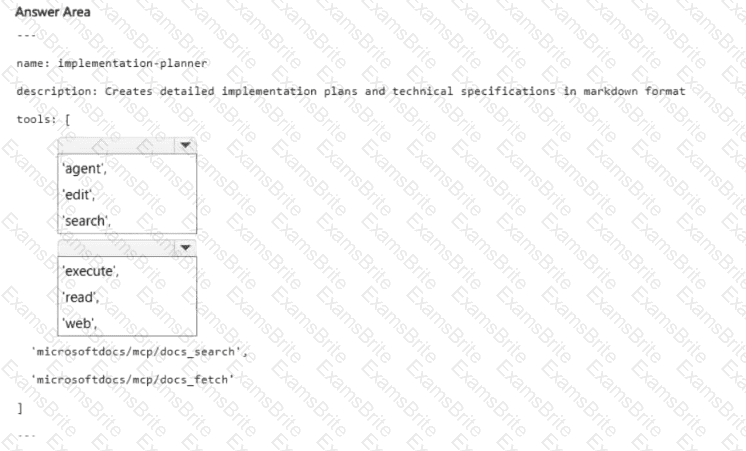
You need to implement agent2 to meet the technical requirements.
How should you complete the YAML configuration? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
HOTSPOT
name: implementation-planner
description: Creates detailed implementation plans and technical specifications in markdown format
tools: [
< Dropdown 1 > ,
< Dropdown 2 > ,
' microsoftdocs/mcp/docs_search ' ,
' microsoftdocs/mcp/docs_fetch '
]
The accompanying image includes empty dropdown controls and recreated practice alternatives.
While upgrading App1, the agent identifies 47 issues, including a security vulnerability, and 46 API incompatibilities across different projects.
Which two actions are unsafe to delegate to the agent and require human involvement? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
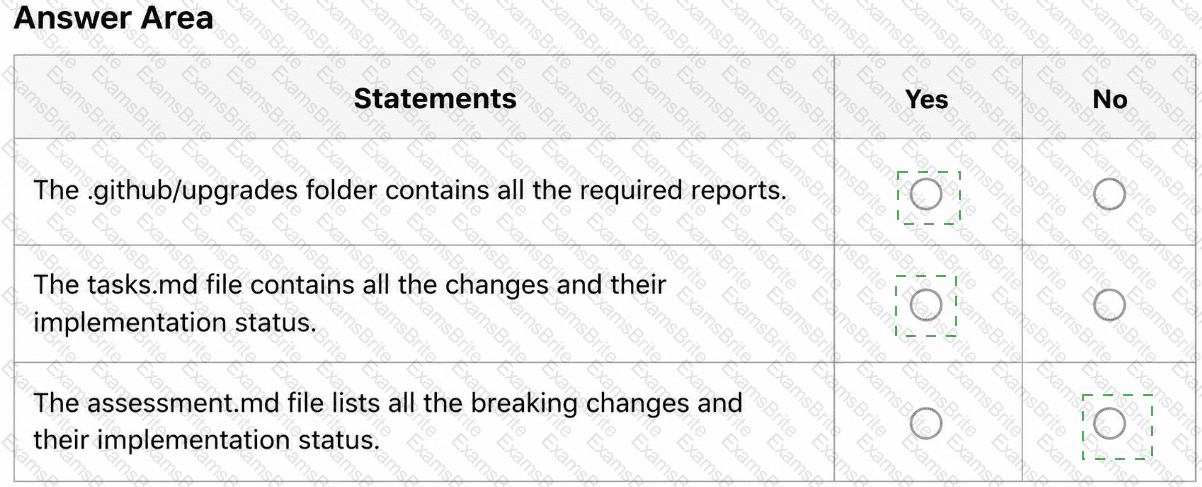
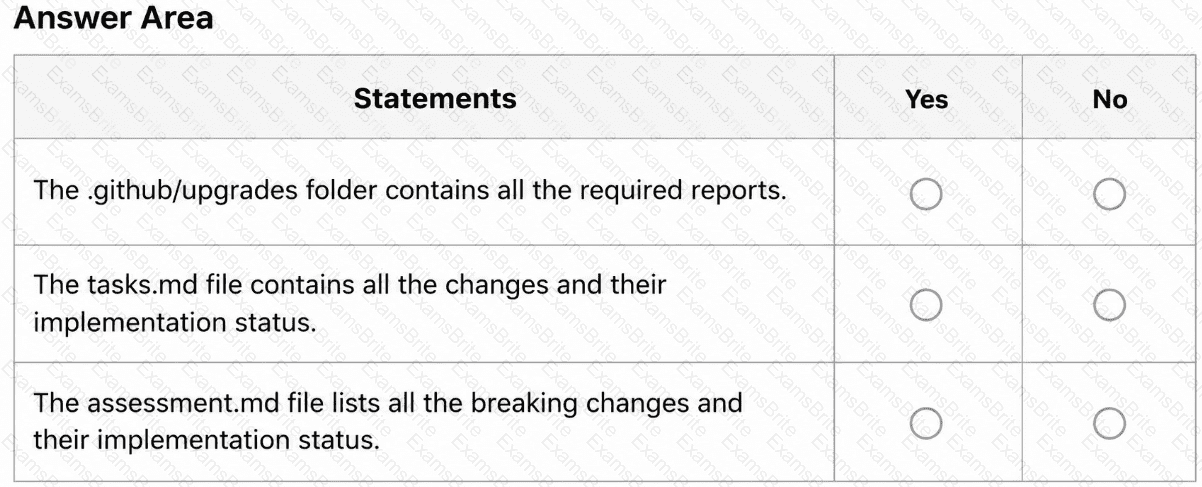
After App1 is upgraded to meet the technical requirements, you need to validate the output.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
You need to troubleshoot the issue reported by Dev1.
What should you review?
You need to configure agent1 to support the planned changes.
What should you do?
You need to resolve the issue of the agents generating conflicting output. The solution must meet the implementation guidelines.
What should you do?
You need to resolve the scoping issue associated to agent1.
What should you do?
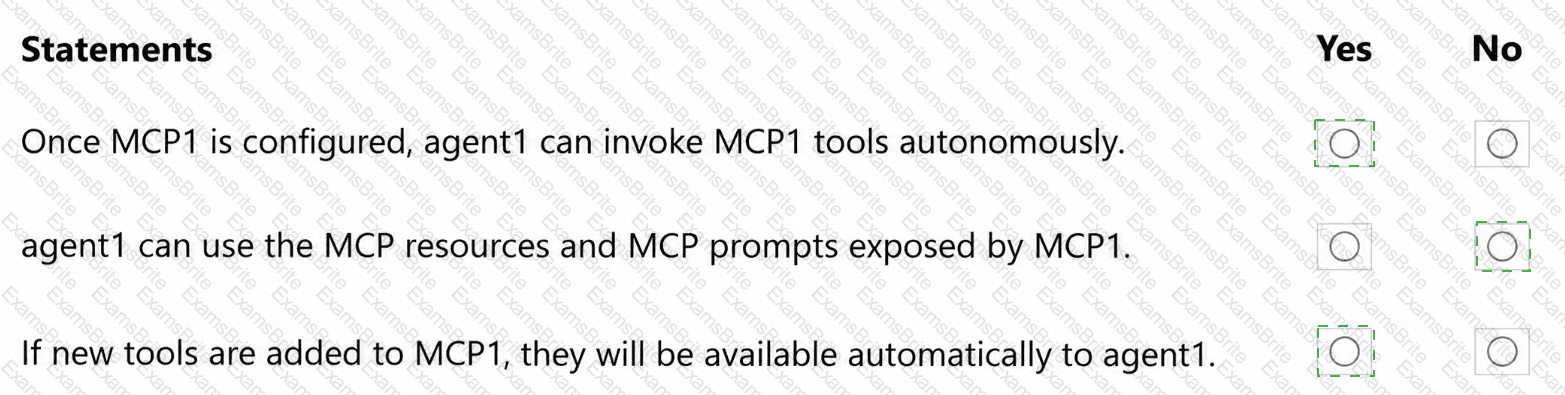
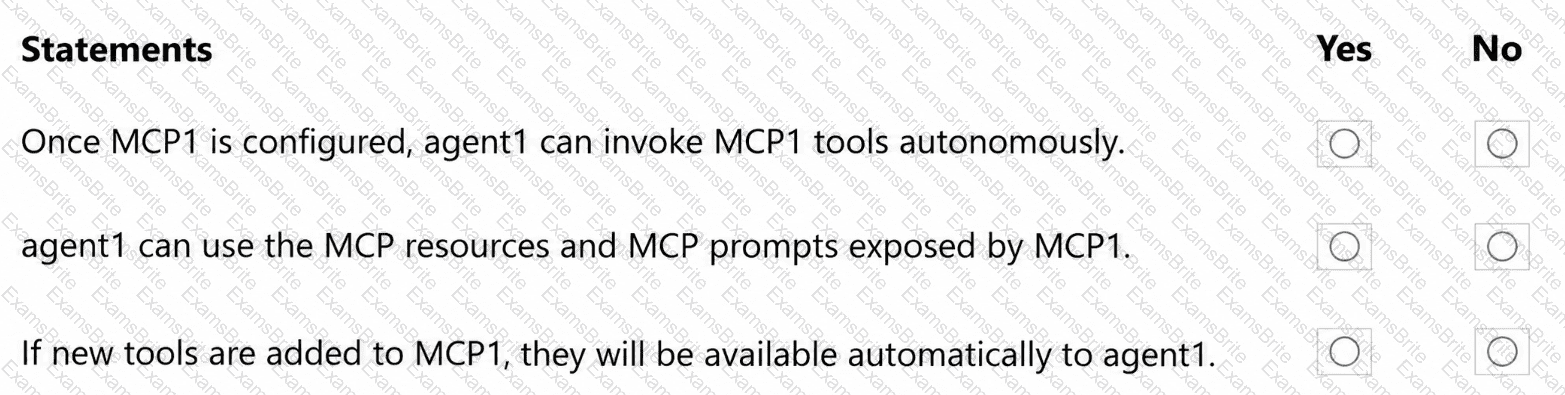
You are evaluating how agent1 will behave after you implement the planned changes.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Before App1 is upgraded, you need to verify each individual upgrade step and whether all tests have passed.
Which file should you use?
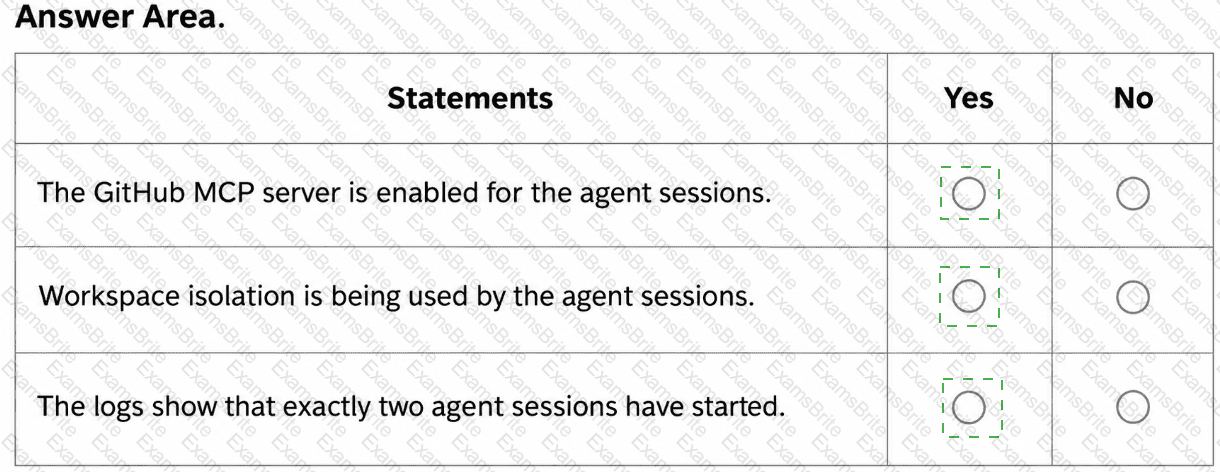
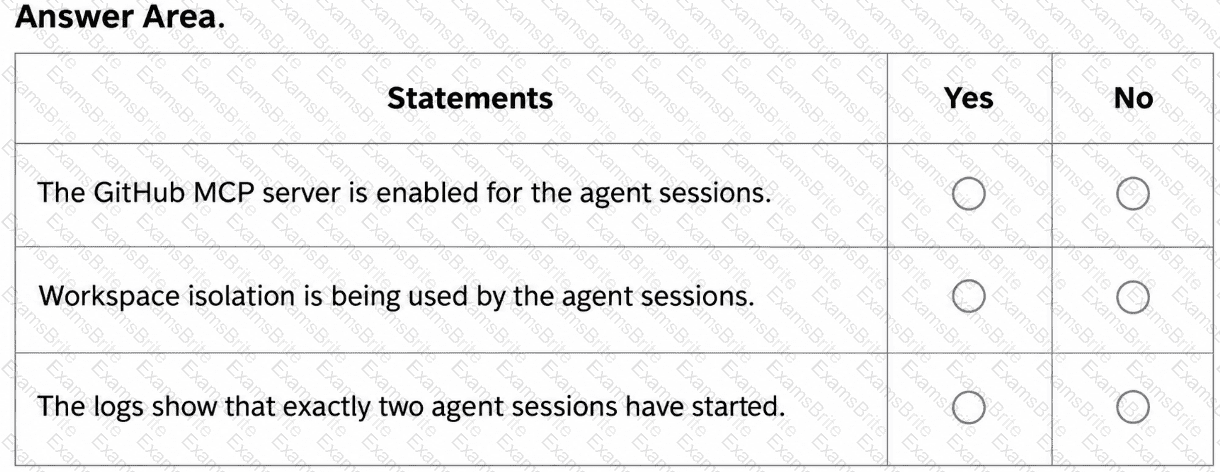
You are evaluating the logs of the multi-agent workflow in repo2.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
You need to make changes to repo1 to support the planned changes for the developers.
What should you modify?
You need to enable Copilot memory to support the planned changes.
What should you configure?
You need to make changes to repo1 to support the planned changes for the agents.
What should you modify?
Your team wants Copilot ' s suggestions to reflect knowledge of internal library APIs that are not publicly documented and not present in the codebase being edited. What is the most appropriate solution?
You have a GitHub Copilot coding agent that has completed a pull request for a security fix in your repository.
Before merging, you need to evaluate the quality of the agent’s work by using both automated evaluation signals and human review.
You review the session log and the pull request.
What are two automated security scanning signals available for the pull request? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
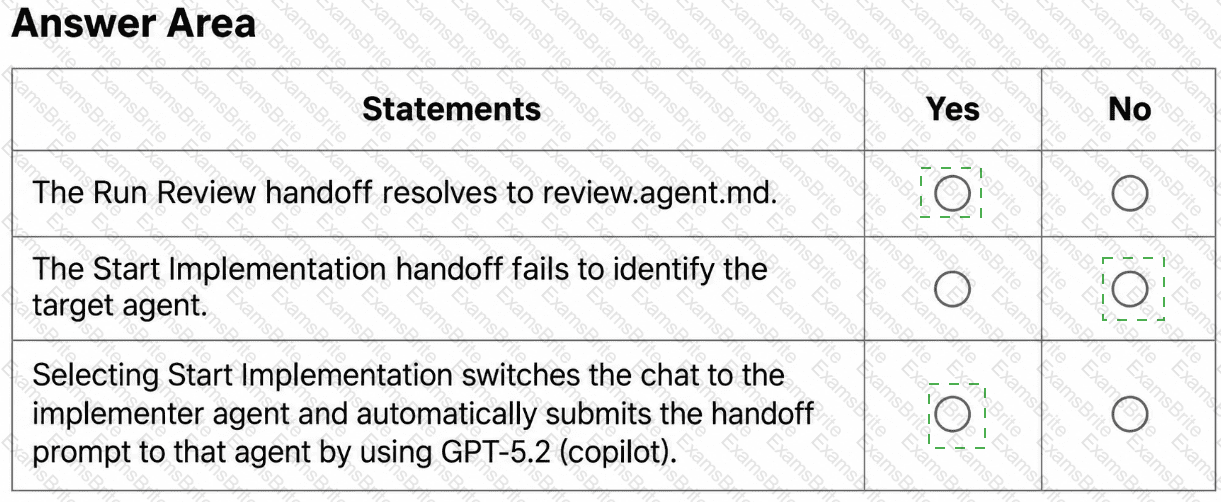
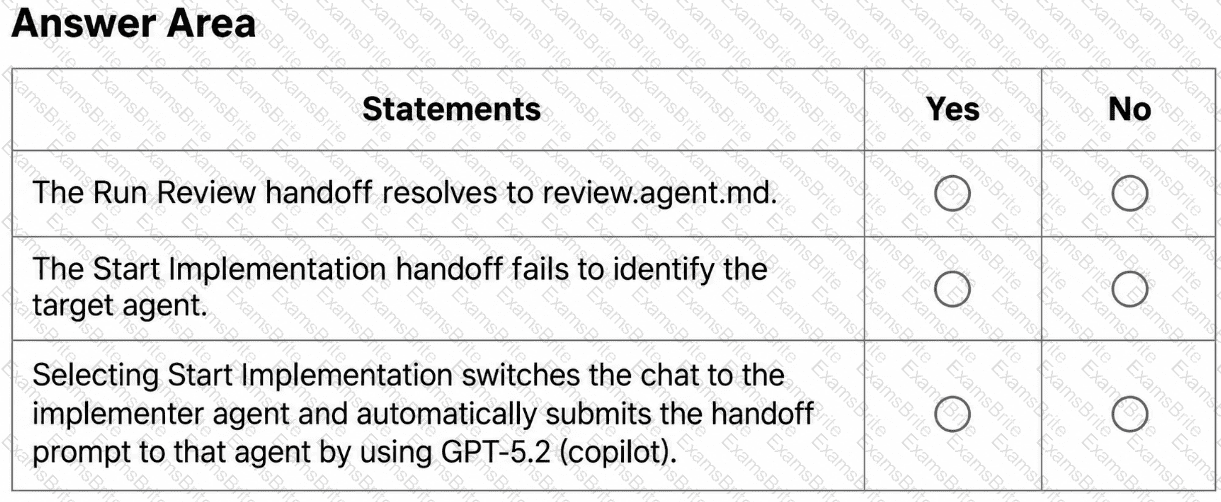
You have a GitHub repository that contains the following custom agent files:
A file named planner.agent.md that includes YAML frontmatter with a handoffs entry that has label: Start Implementation, agent: implementer, and prompt: Now implement the plan outlined above.
A file named implementer.agent.md that is in the same directory as planner.agent.md and includes YAML frontmatter that has name: IMPLEMENTER.
You add a third agent file named review.agent.md that includes name: code-review in the YAML frontmatter.
You make the following changes to planner.agent.md:
Update the existing handoff to include send: true and model: GPT-5.2 (copilot).
Add a second handoff that has label: Run Review, agent: code-review, and prompt: Review the code changes made in the previous step.
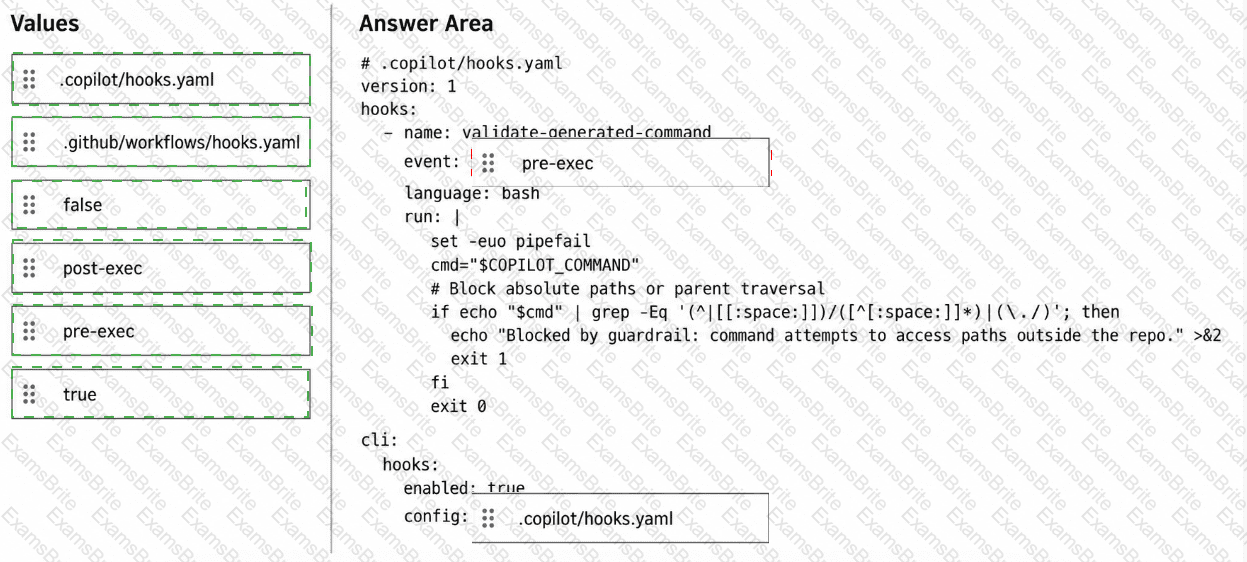
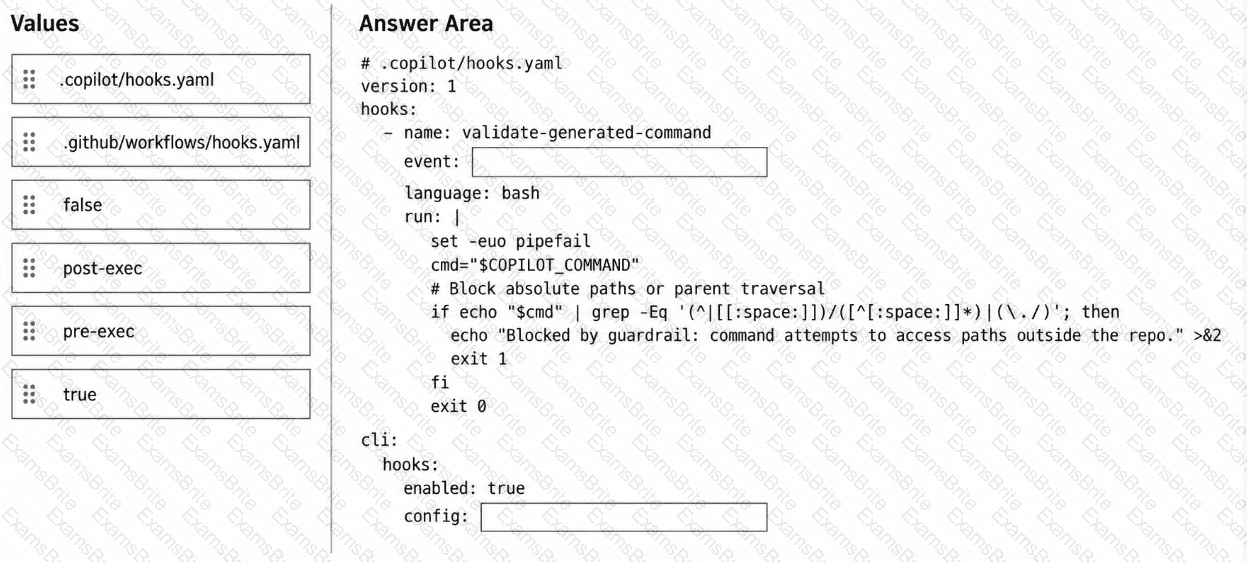
You have a GitHub repository that uses the GitHub Copilot CLI to run autonomous tasks.
You need to validate each generated command before it runs. Any commands that attempt to modify paths outside the repository must be blocked.
How should you complete the YAML? To answer, drag the appropriate values to the correct targets. Each value may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
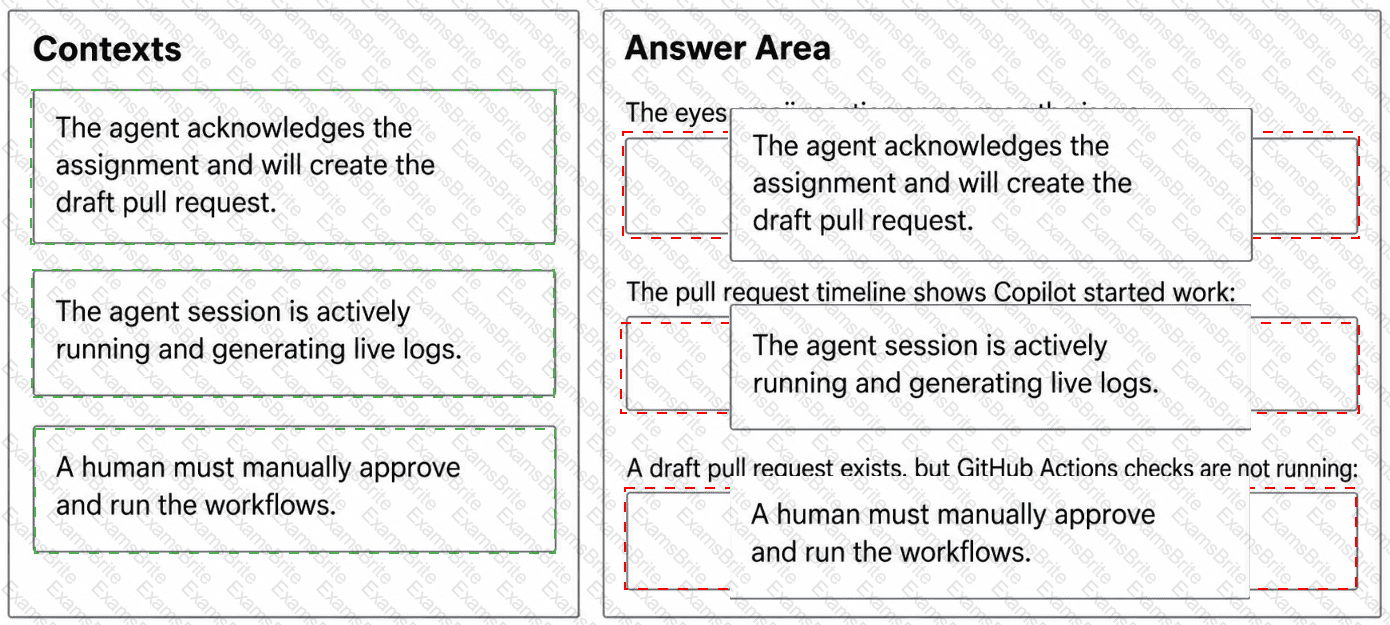
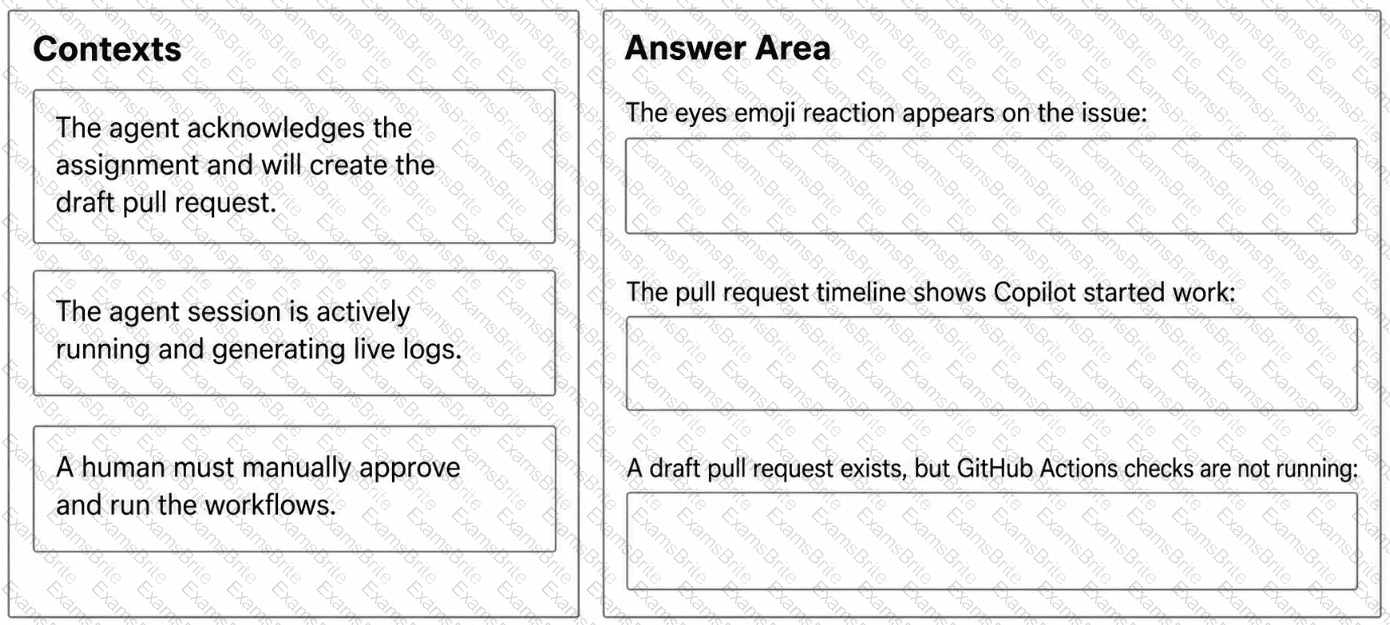
You have a GitHub Enterprise Cloud organization that uses the GitHub Copilot coding agent to resolve issues asynchronously.
When an issue is assigned to GitHub Copilot, the agent creates a draft pull request, but your team cannot always tell whether the agent is actively working, has completed its session, or is awaiting workflow approval.
Which execution context does each signal indicate? To answer, drag the appropriate context to the correct signals.
You want the GitHub Copilot coding agent to follow project-specific conventions (coding style, testing requirements, folder structure) on every task it performs in a repository. What should you create?
You need to provide access to the API key of MCP1. The solution must meet the security requirements.
What should you do?
TESTED 23 Sep 2026