Pre-Winter Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: agile70

ExamsBrite Dumps

Designing and Implementing Enterprise Network Assurance (300-445 ENNA) Question and Answers

Designing and Implementing Enterprise Network Assurance (300-445 ENNA)

Last Update Oct 12, 2026
Total Questions : 117

We are offering FREE 300-445 Cisco exam questions. All you do is to just go and sign up. Give your details, prepare 300-445 free exam questions and then go for complete pool of Designing and Implementing Enterprise Network Assurance (300-445 ENNA) test questions that will help you more.
300-445 pdf

300-445 PDF

$34.5  $114.99
300-445 Engine

300-445 Testing Engine

$40.5  $134.99
300-445 PDF + Engine

300-445 PDF + Testing Engine

$52.5  $174.99
Questions 1

You are investigating intermittent failures in a ThousandEyes transaction test targeting a web application that uses Basic Authentication. The failures occur randomly across different agents and times of day. What steps would you take to troubleshoot and resolve the issue? (Select all that apply)

Options:

A.  

Disable Basic Authentication in the test configuration to isolate the problem.

B.  

Verify the correctness of credentials by manually logging into the application from different locations.

C.  

Analyze the ThousandEyes waterfall charts and HTTP response codes to identify potential bottlenecks or errors.

D.  

Contact the web application vendor to report the issue and inquire about possible server-side problems.

Discussion 0
Questions 2

Which two devices support the Cisco ThousandEyes RoomOS native Endpoint Agent deployment? (Choose two.)

Options:

A.  

Cisco Board Pro

B.  

Cisco TelePresence MX800

C.  

Cisco TelePresence SX20

D.  

Cisco Webex DX80

E.  

Cisco Desk Mini

Discussion 0
Questions 3

An engineer configures an alert on the Cisco Meraki cloud platform that meets these requirements:

The alert must monitor the traffic related to cisco.com on a per-flow basis.

The alert must upload the data to Cisco Meraki for further analysis.

Which type of alert must be used to meet these criteria?
Options:

A.  

Insight Network Health

B.  

Insight WAN Health

C.  

App Webhook Health

D.  

Insight Web App Health

Discussion 0
Questions 4

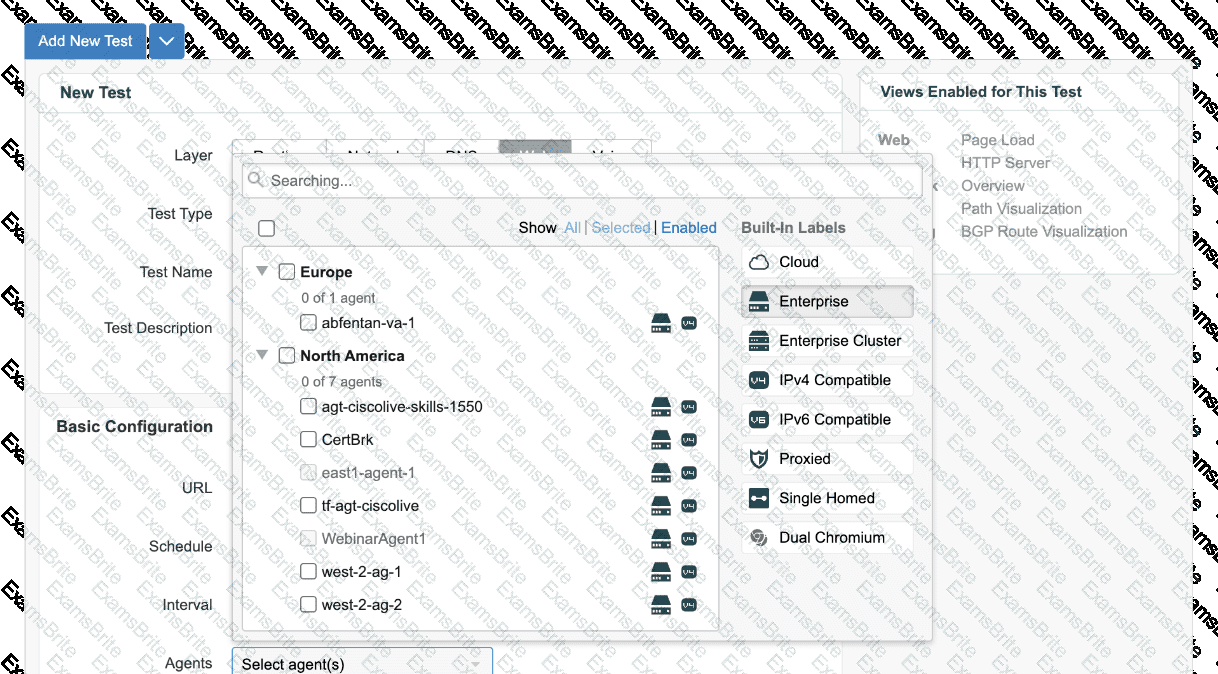
An engineer is trying to configure a Page Load test and is trying to assign the east1-agent-1 to run it, but cannot see that agent listed. What is the reason that the designated agent does not appear?

Options:

A.  

The agent is not running

B.  

The agent is disabled

C.  

The agent is still registering

D.  

The agent does not support Page load tests

Discussion 0
Questions 5

Which command configures the default gateway of an Enterprise Agent for a hosted application within the Cisco Application Hosting Framework in Cisco IOS XE Software?

Options:

A.  

route add default gw 10.0.0.1

B.  

app-default-gateway 10.0.0.1 guest-interface 1

C.  

ip route 0.0.0.0 0.0.0.0 10.0.0.1

D.  

ip default-gateway 10.0.0.1

Discussion 0
Questions 6

A network engineer deploys a ThousandEyes Docker agent on a switch using app-hosting.7 The agent needs to communicate through a proxy server, but this configuration was missed during the initial deployment. The engineer adds the proxy settings to the app-hosting configuration. What is the next step to ensure the agent uses the proxy and appears online in the ThousandEyes portal?

Options:

A.  

Restart the container using app-hosting stop appid agentname followed by app-hosting start appid agentname

B.  

Reinstall the agent using the app-hosting install command with the correct proxy settings

C.  

Execute the full agent lifecycle: app-hosting stop appid agentname, app-hosting deactivate appid agentname, app-hosting activate appid agentname, app-hosting start appid agentname

D.  

No action required; the agent will pick up the configuration automatically

Discussion 0
Questions 7

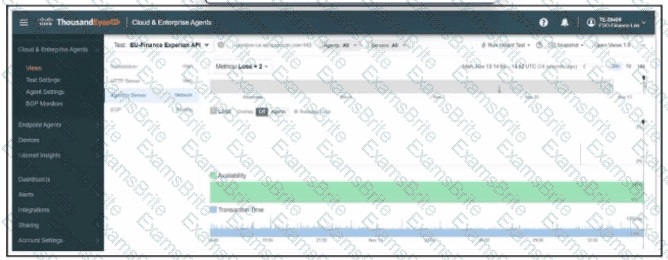
Refer to the exhibit. Which issue is identified in the stream?

Options:

A.  

There was 1% packet loss on November 11.

B.  

There was 1% packet loss on November 12.

C.  

There was 1% packet loss on November 13.

D.  

There was 0% packet loss on November 13.

Discussion 0
Questions 8

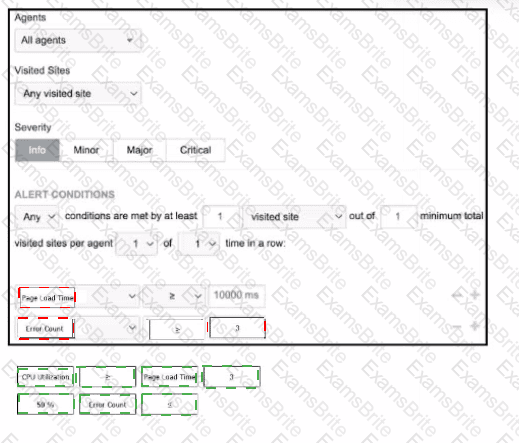
An engineer is configure an alert rule to trigger when employees have issues opening monitored websites in the browsers. Drag and drop the configuration options from the bottom onto the boxes in the alert rule configuration screen. NOT all option are used.
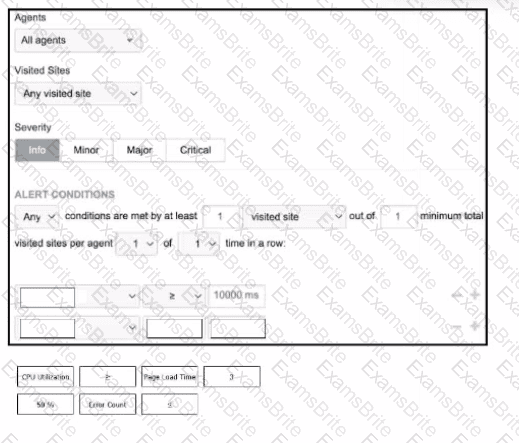
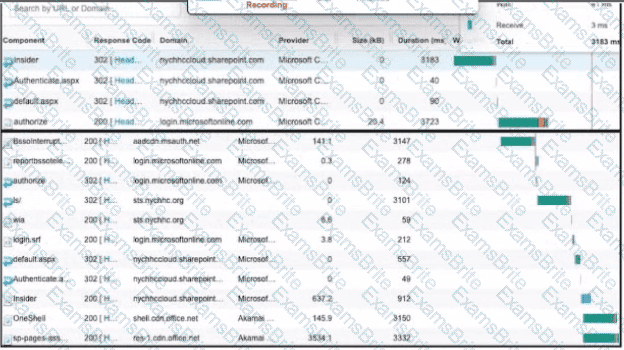
Options:

Discussion 0
Questions 9

Refer to the exhibit. A CiscoThousanflEyes Transactor test is constantly failing Which two actions must the engineer take ' (Choose two.)

Options:

A.  

Validate that the agents DNS resolvers are the same as those used by the workforce

B.  

investigate If DNS issues are occurring from other agents as we

C.  

Generate a DNS trace test using the DNS resolvers set in the agent and measure ONS performance.

D.  

Create a DNS server test using the DNS resolvers and measure those resolver’s performance

E.  

Contact the ISP of that agent’s location to explore DNS performance.

Discussion 0
Questions 10

You ' re responsible for monitoring the performance of a company e-commerce website. You ' re considering using ThousandEyes Synthetic Web Tests. Which of the following functionalities of ThousandEyes Synthetic Web Tests would be MOST beneficial for monitoring the e-commerce checkout process?

Options:

A.  

HTTP server monitoring

B.  

Transaction monitoring

C.  

DNS monitoring

D.  

Routing visibility

Discussion 0
Questions 11

An architect needs to analyze network path metrics from their internal network, specifically from the access layer to a cloud-hosted web server.1 Which ThousandEyes agent is most appropriate for this task?

Options:

A.  

Synthetic Agent

B.  

Enterprise Agent

C.  

Cloud Agent

D.  

Endpoint Agent

Discussion 0
Questions 12

An engineer must track and alert based on a specific response time threshold for the company ' s internal application. Which set of actions must be taken using the Cisco Meraki Insights?

Options:

A.  

Use Network-wide alerts and set a specific response time for internal application.

B.  

Correlate WAN latency and loss against the network performance for the response time.

C.  

Within Insight, Turn off Smart-thresholds for internal application, set a manual threshold, and turn on the alert.

D.  

Within Insight, leverage Smart-thresholds and turn on alerting for that internal application.

Discussion 0
Questions 13

An administrator has set up GPO properly, but realized ThousandEyes EPA was not deployed on one of the office PCs.9 What is the appropriate first step?

Options:

A.  

After GPO deployment, an administrator account must log in to deploy the EPA

B.  

Check that the PC belongs to the needed domain

C.  

Reboot the PC, this will restart GPO on the server

D.  

Reboot the Server, this will restart GPO on the PC

Discussion 0
Questions 14

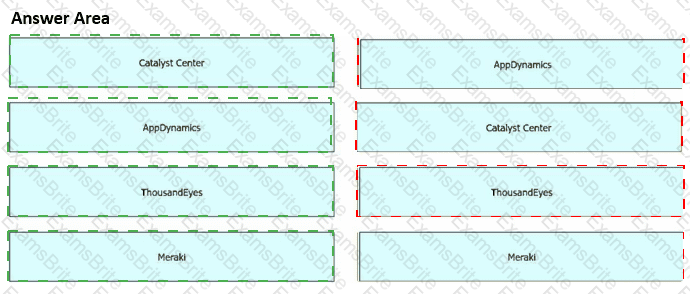
Drag and drop the Cisco Network Assurance platforms from the left onto the corresponding business cases on the right.
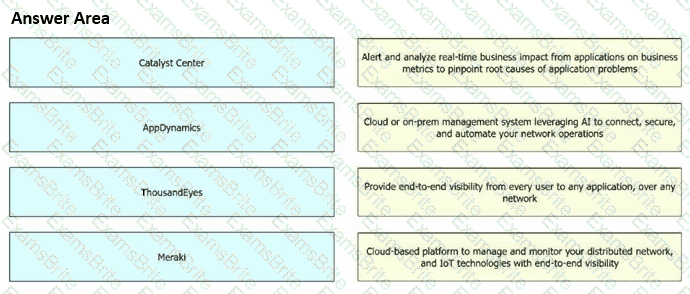
Options:

Discussion 0
Questions 15

What type of endpoint agent test will gather browser activity?

Options:

A.  

Scheduled tests

B.  

Dynamic tests

C.  

Real user tests

D.  

Network Access tests

Discussion 0
Questions 16

Which network assurance platform must be deployed to collect network and application metrics such as latency, transaction time, errors, and completion time for an application hosted by a cloud provider?

Options:

A.  

ThousandEyes

B.  

AppDynamics

C.  

Meraki

D.  

Catalyst Center

Discussion 0
Questions 17

Which of the following metrics can be used to configure an alert rule for Endpoint Agent HTTP Server tests? (Choose two)
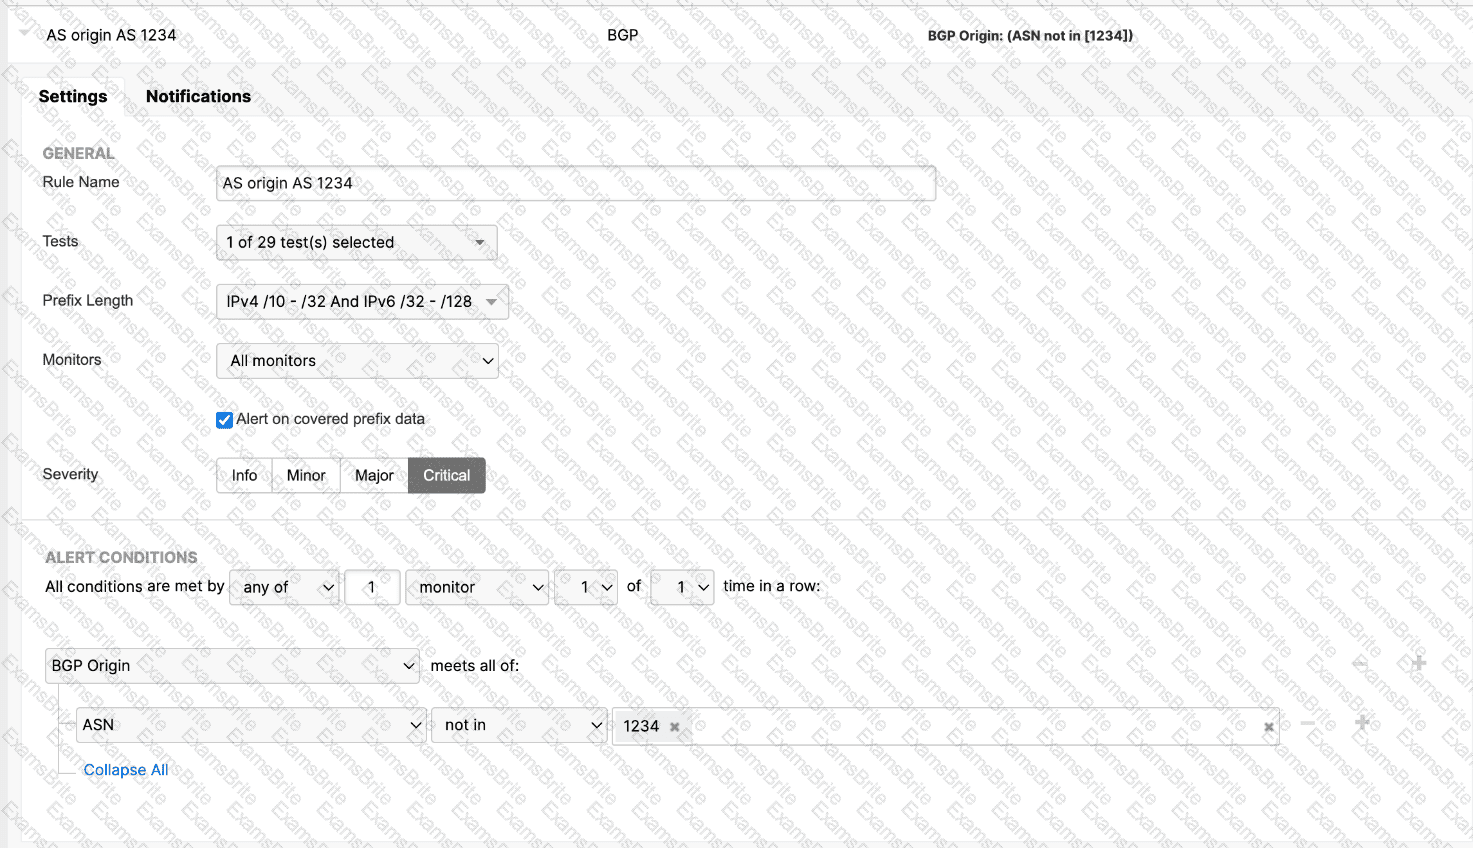
Options:

A.  

Response Time

B.  

BGP Reachability

C.  

Error Type

D.  

Interface Throughput

Discussion 0
Questions 18

An engineer needs to create a test to execute a user ' s workflow where the user has to log in to OneDrive and download a file. The test has to implement a retry mechanism. The engineer has limited scripting experience. What are the actions that the engineer needs to take?

Options:

A.  

Create the script from the Office365 > OneDrive - Download File template

B.  

Install the ThousandEyes Recorder IDE and record the user flow

C.  

Check the transaction-scripting-examples repository for sample scripts

D.  

All of the above

Discussion 0
Questions 19

Refer to the exhibit.

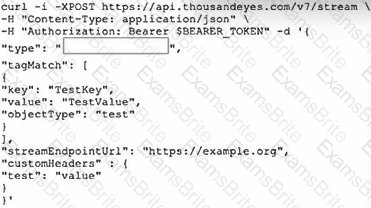
Which integration type should be configured between ThousandEyes and Grafana?

Options:

A.  

opentelemetry

B.  

custom-webhook

C.  

push-api

D.  

poll-api

Discussion 0
Questions 20

A global retail company is using Cisco AppDynamics for application performance monitoring and Cisco ThousandEyes for network intelligence. The IT operations team is struggling with alert fatigue and wants to streamline its incident management process. These are the requirements:

Consolidate alerts from both AppDynamics and ThousandEyes into a single platform.

Quickly correlate application issues with potential network problems.

Which integration feature meets these requirements?

Options:

A.  

AppDynamics Bi-Directional Integration with ThousandEyes test recommendations

B.  

AppDynamics synthetic transaction monitoring with ThousandEyes network

C.  

ThousandEyes Network Intelligence integration with AppDynamics Dash Studio

D.  

ThousandEyes alert notifications service integration with AppDynamics

Discussion 0
Questions 21

Refer to the exhibit.

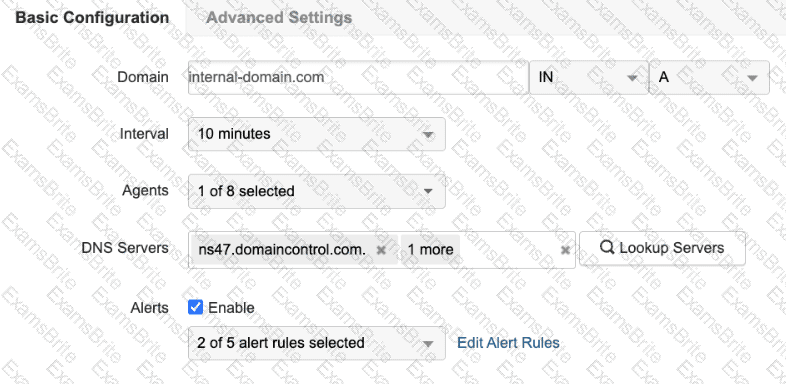
A network admin has been tasked with monitoring the IPv6 record and name server resolution times with different agents. Select the two actions that the engineer must take to meet the requirements.
Options:

A.  

Create a DNS Server test monitoring the A record

B.  

Create a DNS Server test monitoring the AAAA record

C.  

Create a DNS Trace test monitoring the ANY record

D.  

Create a DNS Server test monitoring the NS record

E.  

Create a DNS Trace test monitoring the NS record

Discussion 0
Questions 22

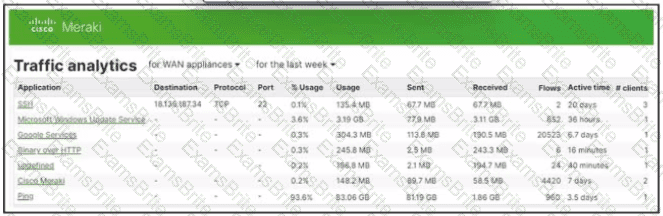
Refer to the exhibit. An engineer is troubleshooting reported network delays that users are experiencing in Cisco Meraki. Which configuration must be implemented to resolve the issue?

Options:

A.  

firewall rule to block SSH and WSUS traffic

B.  

firewall rule to block SSH traffic

C.  

quality of service rule to limit the SSH and WSUS traffic

D.  

firewall rule to block ICMP traffic

Discussion 0
Questions 23

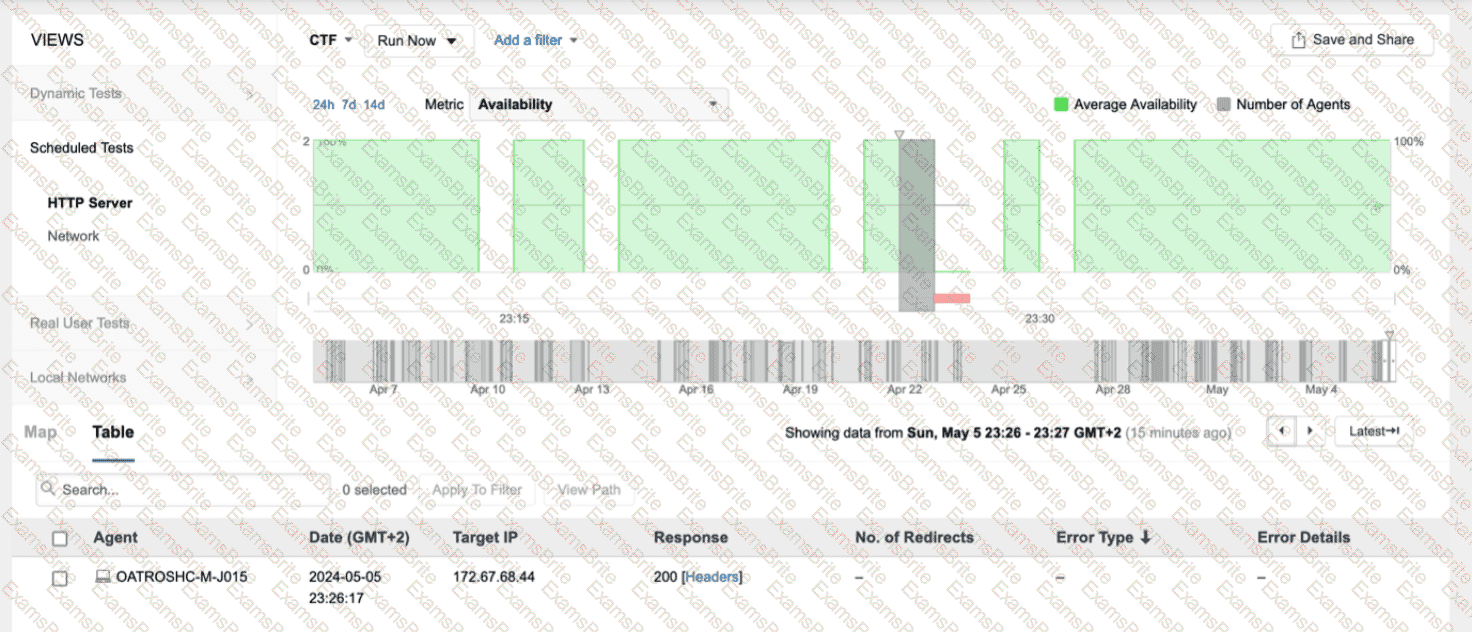
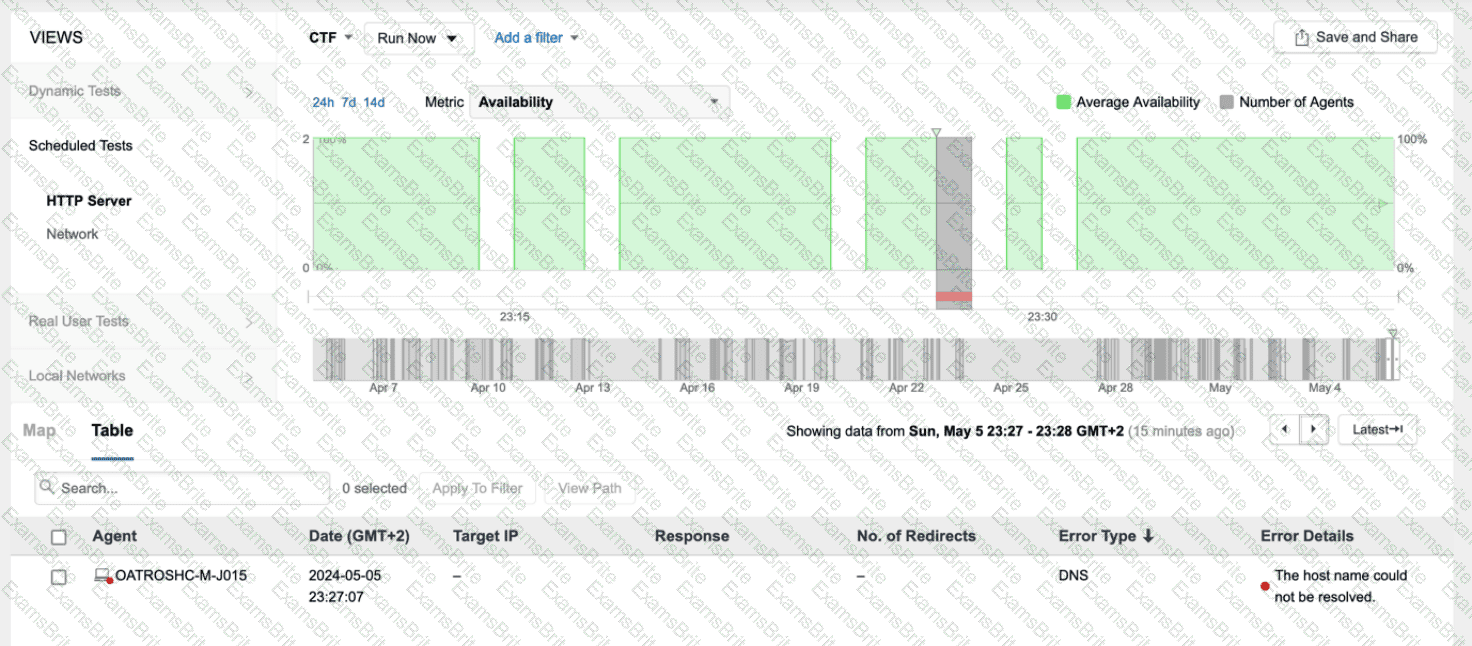
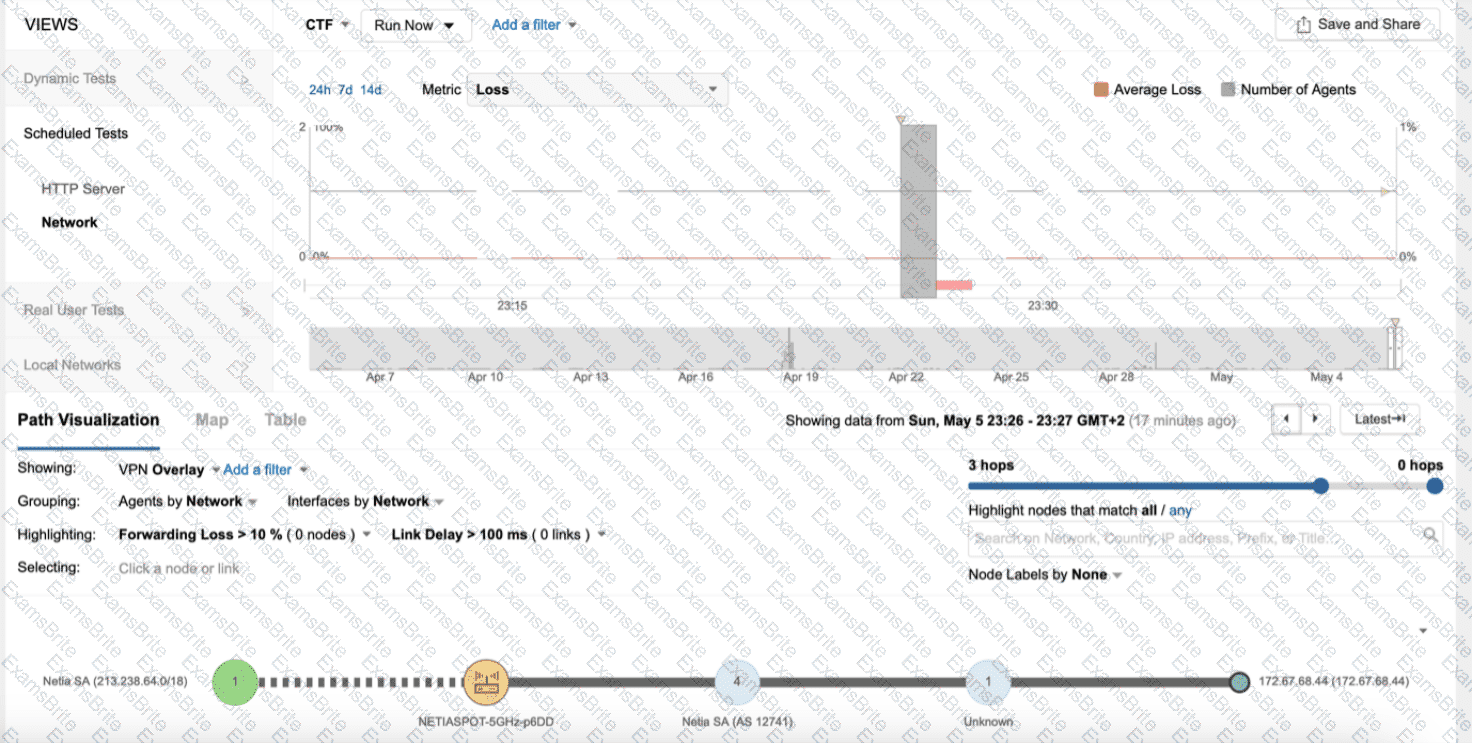
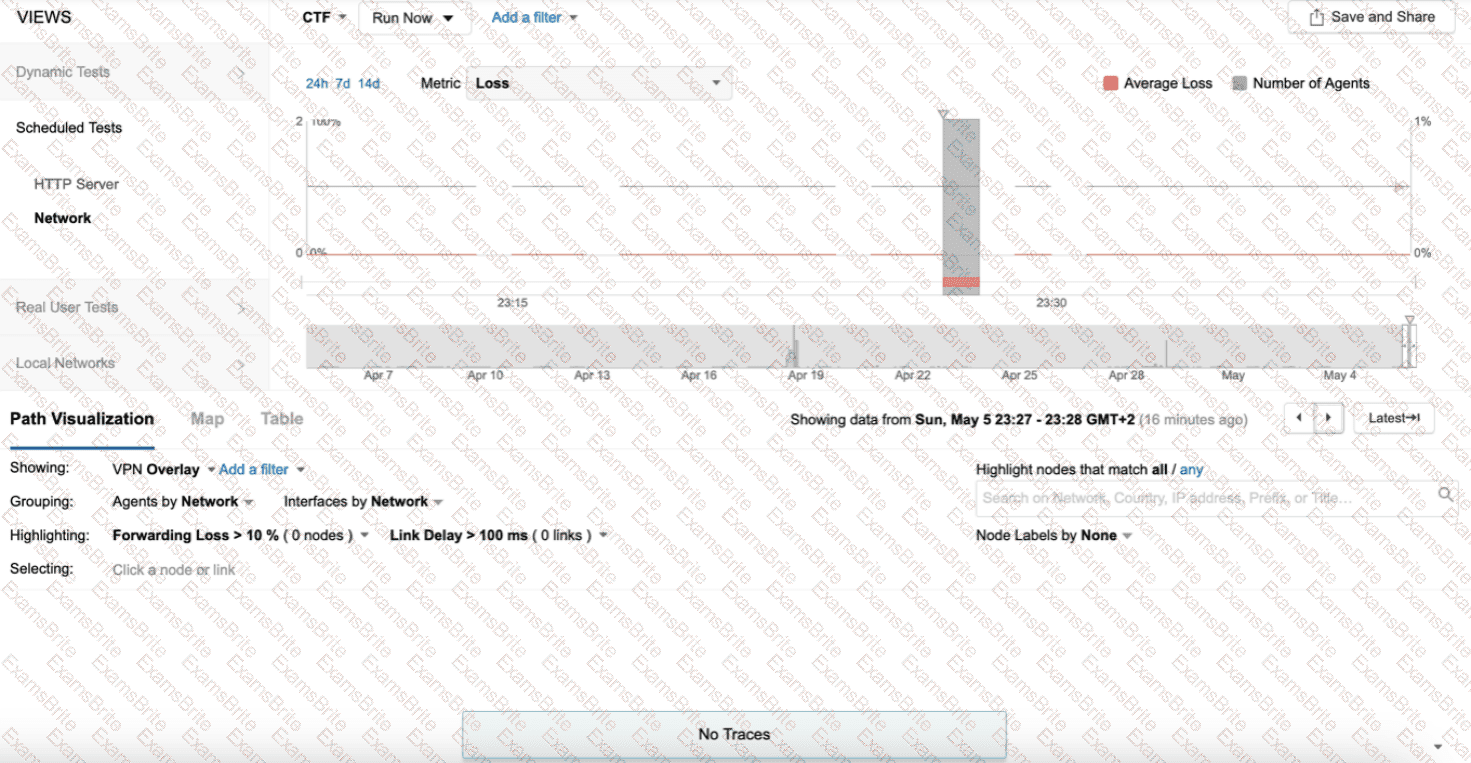
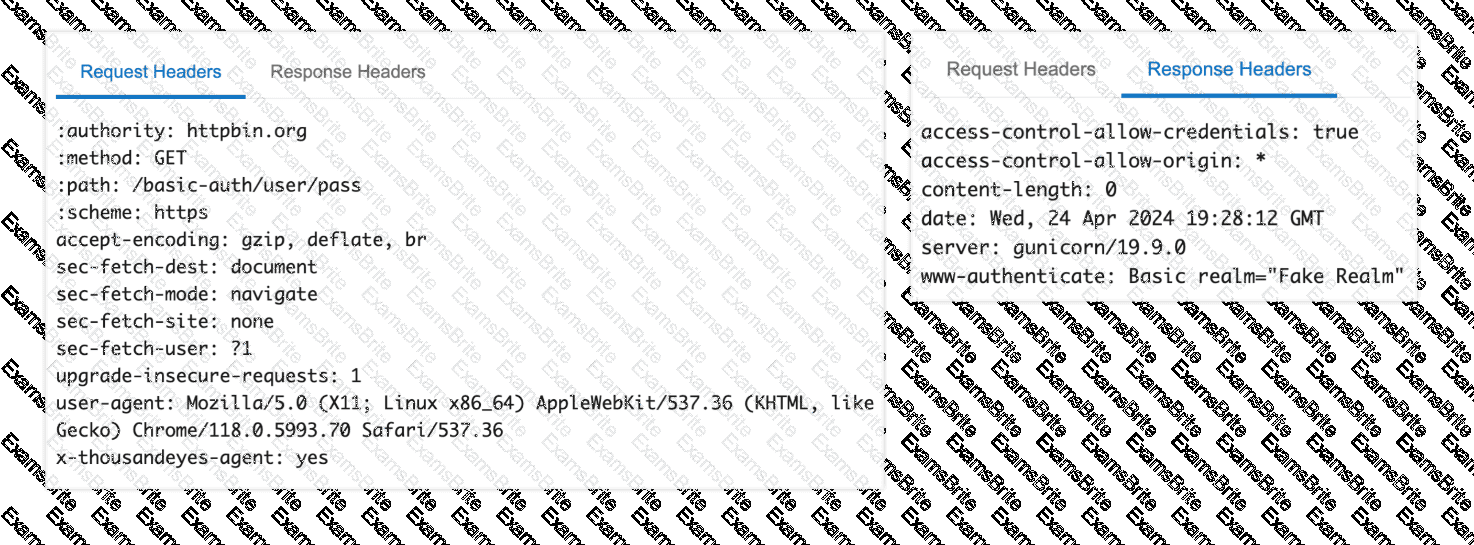
Refer to the exhibits.

The endpoint has the following IP credentials:

192.168.100.9/24, DNS: 8.8.8.8, 8.8.4.4, GW: 192.168.100.1

Based on the views presented in the exhibits, what led to the error occurring on Sun, May 5 23:27 GMT +2?

Options:

A.  

The test target stopped responding.

B.  

The FQDN of the test target is non-existent.

C.  

The DNS servers assigned to the endpoint are unreachable.

D.  

The DNS settings on the endpoint are incorrect.

Discussion 0
Questions 24

What type of agent is typically installed on Cisco SD-WAN devices as part of the ThousandEyes integration with vManage?

Options:

A.  

Cloud Agent

B.  

Browser Agent

C.  

Enterprise Agent1

D.  

Endpoint Agent2

Discussion 0
Questions 25

How would a user without coding knowledge write a transaction script to monitor a user workflow?

Options:

A.  

Use the built-in Chrome developer tools and export the generated file to the ThousandEyes platform.

B.  

Use the recorder feature in the ThousandEyes Endpoint browser extension to capture a user session.

C.  

Use the ThousandEyes Recorder IDE to record the user journey and export it to the Cisco ThousandEyes platform.

D.  

Download the HAR (HTTP Archive) file of each page in the transaction flow and export it to the ThousandEyes platform.

Discussion 0
Questions 26

Considering the observed network behavior and the information in the exhibits, which action would be the most appropriate next step for the network administrator to take?

Options:

A.  

Contact the internal network team to investigate potential misconfigurations on the local routers

B.  

Reach out to the Internet Service Provider (ISP) to report the suspected BGP hijacking incident

C.  

Implement traffic filtering rules on the firewall to block traffic originating from AS 10297

D.  

Restart the DNS server to refresh its cache and potentially resolve the observed issue

Discussion 0
Questions 27

An engineer works for a restaurant chain that runs the Cisco ThousandEyes Enterprise Agent on Meraki MX devices. The engineer must set up monitoring for a web application that requires users to authenticate with the Basic authentication scheme. Which action must the engineer take to configure the monitoring for this application?

Options:

A.  

Set up a Page Load test with Basic HTTP authentication enabled.

B.  

Set up a Web Transaction test with Basic HTTP authentication enabled.

C.  

Set up an HTTP Server test with Basic HTTP authentication enabled.

D.  

Set up a Web Transaction test that fills the credentials in the interactive form and submits the form.

Discussion 0
Questions 28

ThousandEyes offers several native integrations for receiving instant event notifications triggered by alerts. Which of the following integrations are available directly within the ThousandEyes platform? Select all that apply.

Options:

A.  

ServiceNow

B.  

PagerDuty

C.  

MS Teams

D.  

Splunk

E.  

AWS

F.  

AppDynamics

G.  

Webex

Discussion 0
Questions 29

The network team has deployed Webex RoomOS Endpoint Agents and integrated Webex Control Hub with ThousandEyes. The VoIP team wants to know which metrics they can collect from the Webex Control Hub view. Where does the VoIP team find the network data?

Options:

A.  

Devices

B.  

Network Path

C.  

Users

D.  

Settings

Discussion 0
Questions 30

Which action must be taken first in the Connect ThousandEyes task when integrating Cisco Meraki dashboard and Cisco ThousandEyes?

Options:

A.  

Paste the Account Group token from ThousandEyes into the Meraki dashboard.

B.  

Paste the ThousandEyes API token into the Meraki Dashboard.

C.  

Paste the Meraki Dashboard API into ThousandEyes.

D.  

Log in to ThousandEyes with the same username used to log in to the Meraki Dashboard.

Discussion 0
Questions 31

The Endpoint stopped appearing online after it was moved to another network. The customer reviewed the endpoint logs but did not identify anything suspicious. The customer also confirmed that the endpoint was online on the old network, and the new network is fully operational. Other endpoints that were moved to the new network are also online. Since the new network is small, the admin is using static IP assignment. What is the best way to bring the endpoint online?
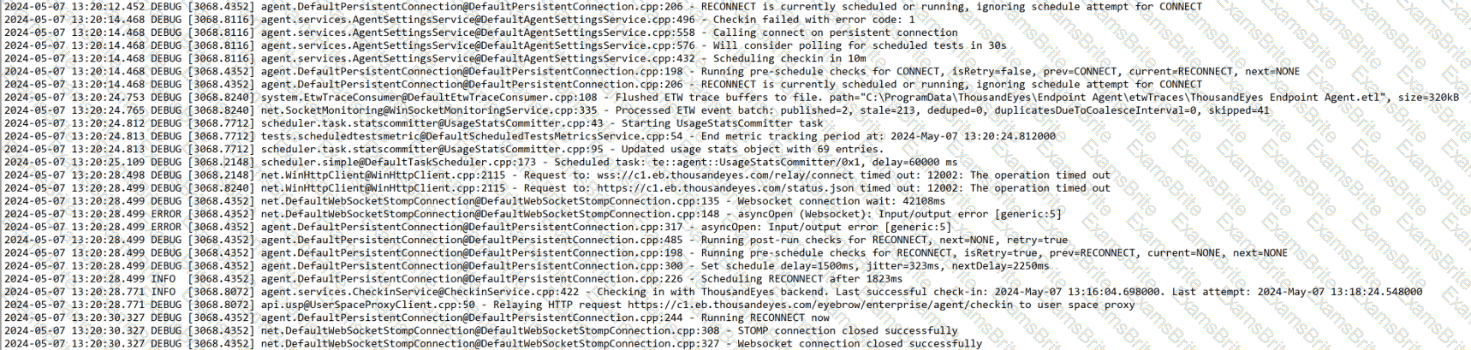
Options:

A.  

It may be an issue with the lack of space in the new network. The endpoint should be moved back to the old network.

B.  

The endpoint agent should be reinstalled to come online. This always helps.

C.  

The endpoint will automatically come online in 10-15 minutes, no action is needed.

D.  

Endpoint IP settings must be checked along with connectivity to c1.eb.thousandeyes.com.

Discussion 0
Questions 32

What is an important consideration when choosing a time period for collecting data to establish a baseline for interface utilization on a critical network link?

Options:

A.  

Selecting the time period with the lowest network traffic volume.

B.  

Ensuring the time period aligns with the organization ' s financial year.

C.  

Capturing both peak and off-peak traffic patterns for a representative view.

D.  

Limiting the time period to minimize the amount of data that needs to be analyzed.

Discussion 0
Questions 33

The following exhibit shows the Capacity Planning results for a router interface connected to an ISP, which provides a 1Gbps connection. Based on the evidence, which action is most likely to fix the observed behavior?
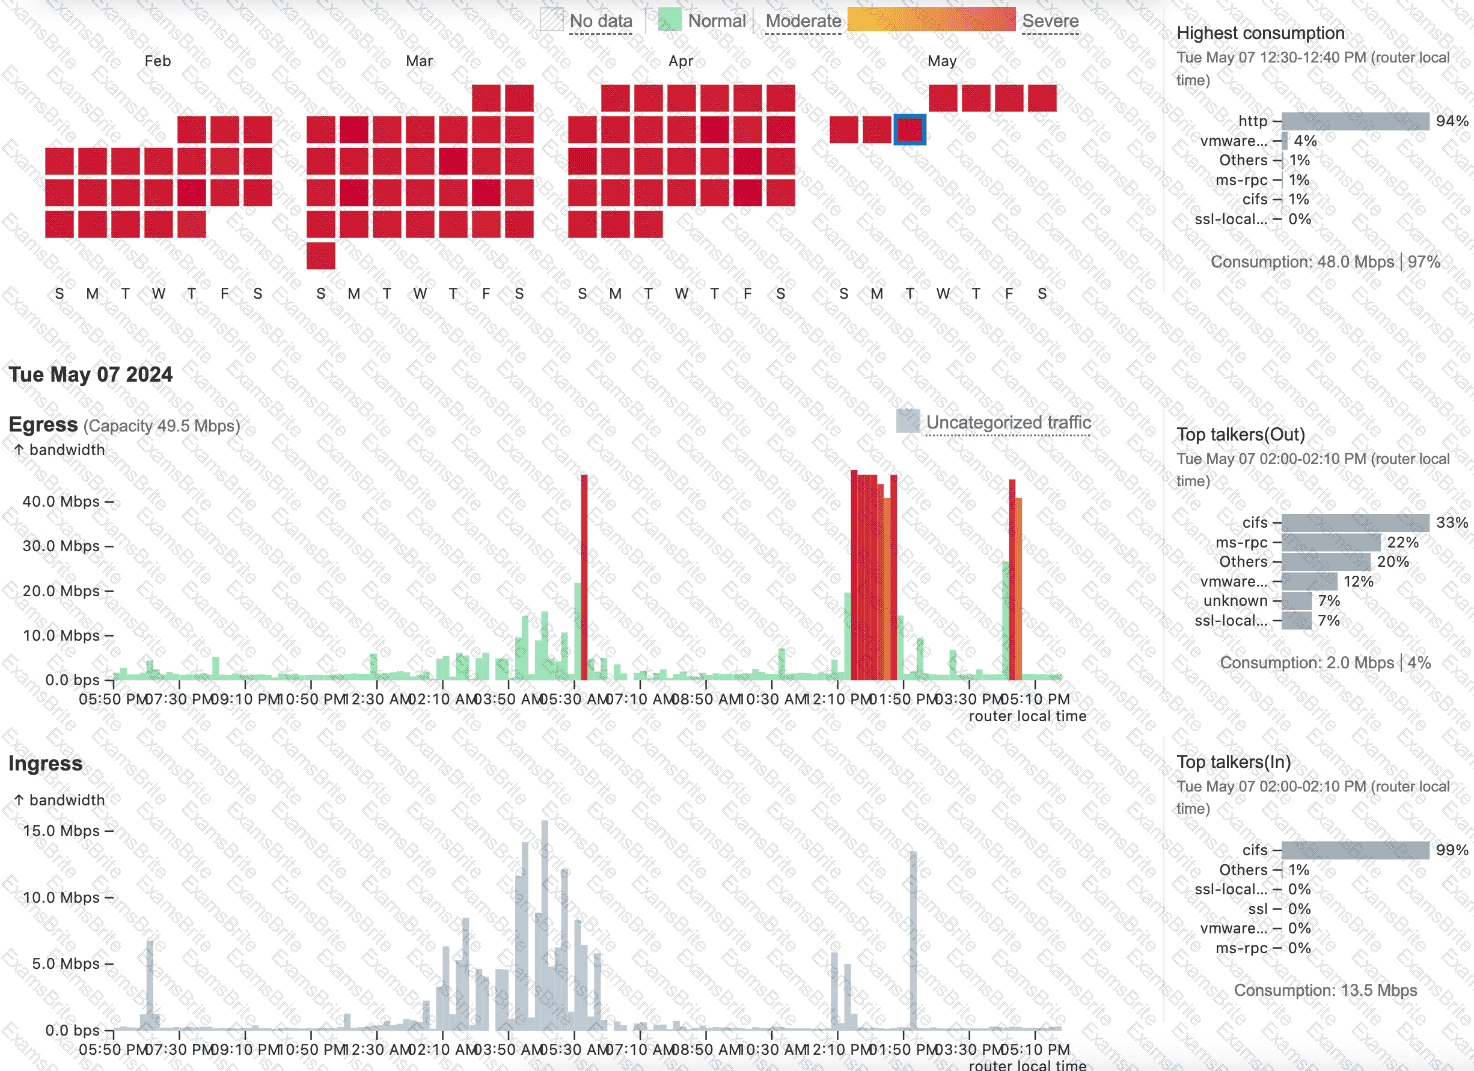
Options:

A.  

Request a link increase from the ISP

B.  

Reconfigure maximum capacity for the interface

C.  

Restrict the Web Sites that can be visited from the site

D.  

Reconfigure business hours settings

Discussion 0
Questions 34

Which type of test are we using for these dashboards (Executive and IT Operations)?

Options:

A.  

HTTP server

B.  

Page Load

C.  

Agent to server

D.  

FTP

Discussion 0
Questions 35

Review the exhibits. Based on the evidence, which action is most likely to solve the issue?
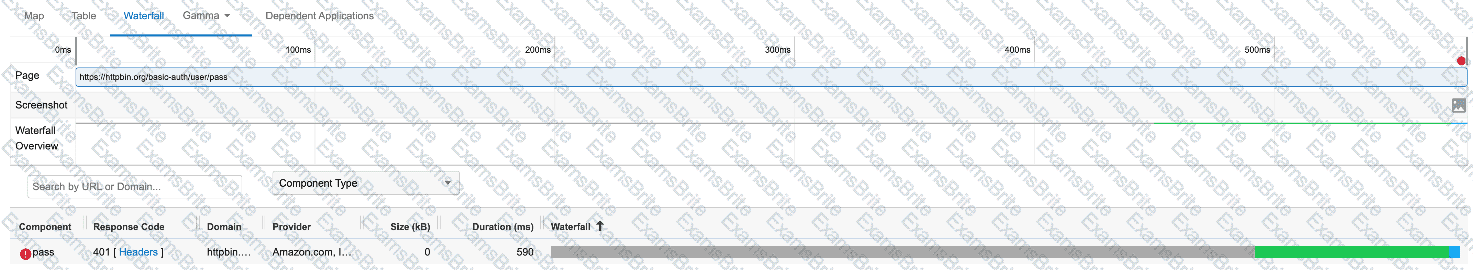
Options:

A.  

Modify the firewall rules to allow connections to the target domain

B.  

Modify the authentication credentials

C.  

Change the HTTP request method to PATCH

D.  

Modify the target URL to an available API endpoint

Discussion 0